

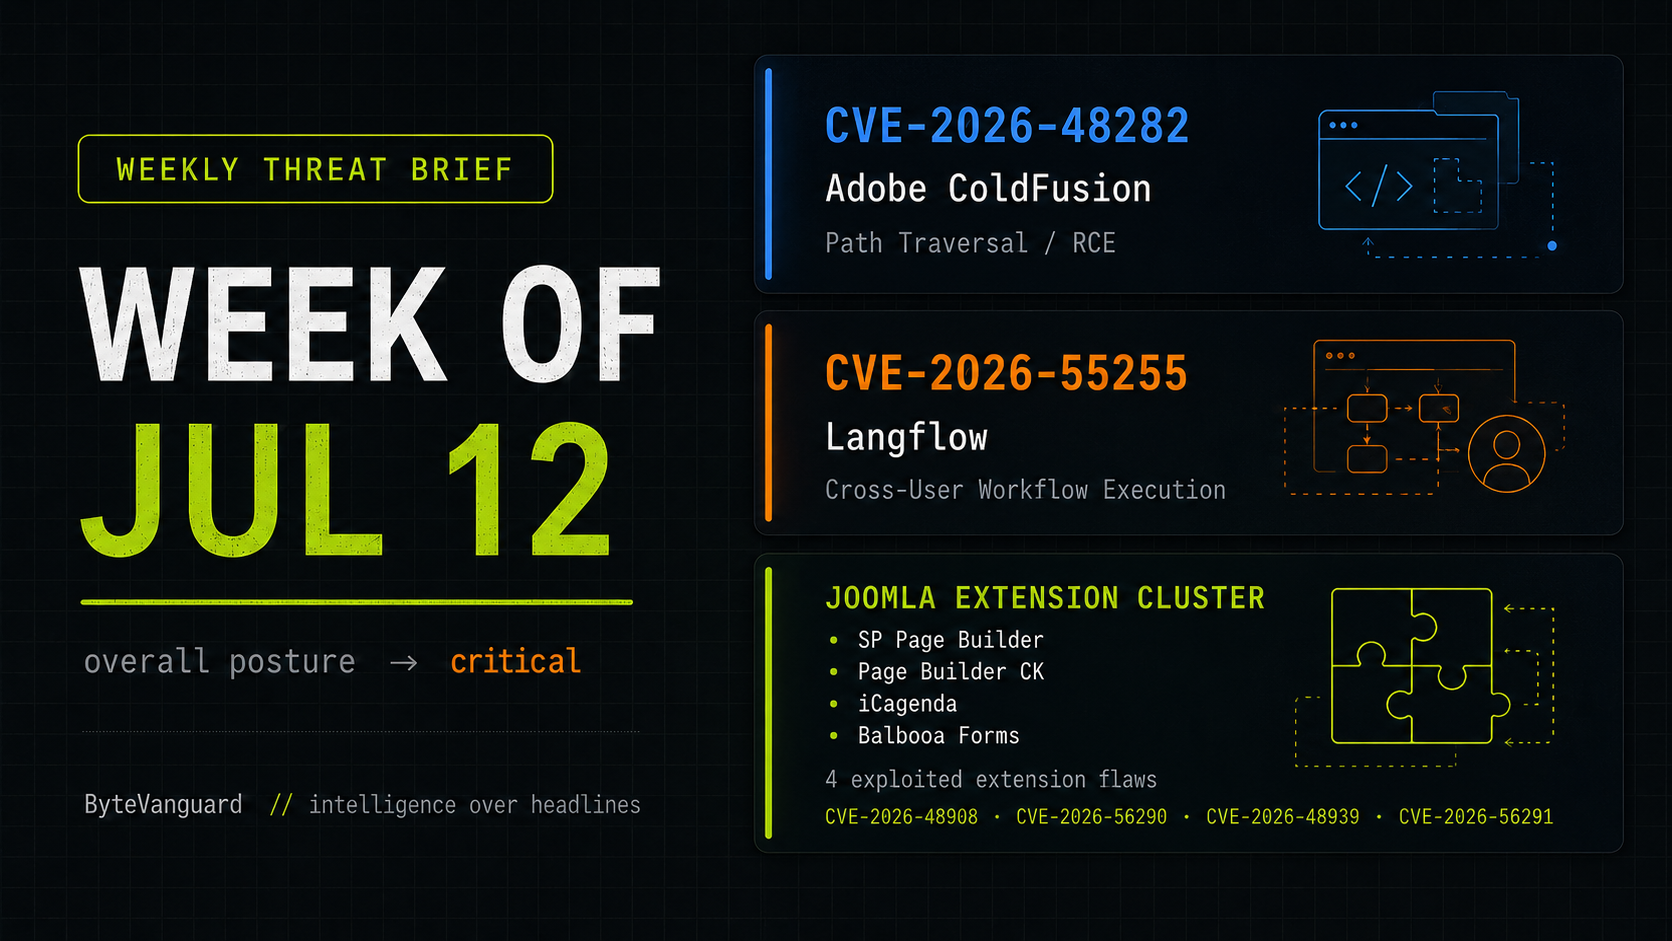
Week Ending: July 12, 2026 | Overall Risk Posture: Critical
CISA added six vulnerabilities to the Known Exploited Vulnerabilities catalog during the week ending July 12: four affecting Joomla extensions, one affecting Adobe ColdFusion, and one affecting Langflow.
Five can lead to code execution. The four Joomla flaws abuse file-upload functionality, while the ColdFusion vulnerability uses path traversal to reach arbitrary code execution. Langflow allows one authenticated user to execute another user’s workflow.
The common issue is not one vendor or technology. It is application functionality crossing into execution. Upload forms, file paths, and workflow identifiers become security boundaries when they control what the platform stores, retrieves, or runs.
Threat at a Glance
| Area | Key Issue | Defender Priority |
|---|---|---|
| Joomla Extensions | Four exploited upload flaws affect page builders, an event manager, and a form extension. | Inventory extensions, update affected versions, and inspect upload directories for malicious files. |
| Adobe ColdFusion | CVE-2026-48282 allows unauthenticated path traversal leading to arbitrary code execution. | Install ColdFusion 2025 Update 10 or 2023 Update 21 and review the server for compromise. |
| Langflow | CVE-2026-55255 allows an authenticated user to execute another user’s flow. | Upgrade to Langflow 1.9.1 or later and review shared or multi-user deployments. |
| Remediation Window | The additions carried three-day federal remediation deadlines. | Treat exposed systems as emergency work rather than waiting for normal patch cycles. |
Active Exploitation and Immediate Risk
-
Joomla extension cluster
Four separate Joomla extensions entered KEV this week:
CVE-2026-48908 affects JoomShaper SP Page Builder through version 6.6.1. The issue permits unauthenticated file upload and remote code execution. Version 6.6.2 contains the fix.
CVE-2026-56290 affects Joomlack Page Builder CK and also allows unauthenticated file upload leading to code execution.
CVE-2026-48939 affects iCagenda attachment handling. Fixed releases include 3.9.15 and 4.0.8.
CVE-2026-56291 affects Balbooa Forms through version 2.4.0. Version 2.4.1 addresses the flaw.
Together, the four additions show why extension-level inventory matters. Knowing that a server runs Joomla is not enough when the vulnerable code sits in optional components. -
Adobe ColdFusion code execution
CVE-2026-48282 is an unauthenticated path traversal vulnerability affecting ColdFusion 2025 Update 9 and earlier and ColdFusion 2023 Update 20 and earlier.
Adobe assigned the vulnerability a CVSS score of 10.0 and reported limited active exploitation. Successful exploitation can execute code in the context of the ColdFusion service account, placing application files, credentials, databases, and internal integrations at risk. -
Langflow cross-user workflow execution
CVE-2026-55255 affects Langflow versions earlier than 1.9.1.
The vulnerable endpoint accepts a flow identifier without consistently verifying that the authenticated user owns the requested flow. An attacker with a valid account can execute another user’s workflow, potentially exposing processed data or consuming connected resources.
Common Failure Patterns
-
Incomplete software inventories
Asset tools often identify the main platform but miss extensions, plugins, and development components. This creates blind spots where vulnerable functionality remains exposed. -
File uploads stored where code can execute
Upload flaws become critical when user-supplied files are placed inside web-accessible directories and interpreted by the server. -
Weak object-level authorization
Langflow shows that authentication alone is not enough. Every request must also verify that the user is authorized to access or execute the specific object being requested. -
Patching without investigation
Installing an update closes the vulnerability but does not remove web shells, unauthorized accounts, altered files, or stolen credentials created before remediation.
Defender Priorities
-
Inventory Joomla extensions
Check production, development, archived, regional, and vendor-managed sites. Record the extension name and version, not only the Joomla core release. -
Apply the available updates
Update SP Page Builder to 6.6.2 or later, iCagenda to 3.9.15 or 4.0.8 or later, Balbooa Forms to 2.4.1 or later, and Page Builder CK to the latest vendor-patched release. -
Inspect web servers for persistence
Review upload folders, templates, temporary directories, and web roots for unexpected PHP files. Check for new administrator accounts, modified extensions, and suspicious outbound connections. -
Patch ColdFusion and review its environment
Install ColdFusion 2025 Update 10 or ColdFusion 2023 Update 21. Confirm the update succeeded and investigate unusual files, processes, scheduled tasks, and application-server activity. -
Upgrade Langflow
Move to version 1.9.1 or later. Review deployments where multiple users or teams share one instance, especially where workflows connect to APIs, models, databases, or cloud services. -
Rotate exposed credentials when necessary
If compromise is suspected, rotate administrator passwords, API keys, database credentials, service tokens, and other secrets available to the affected platform.
Signals to Watch
-
Continued targeting of CMS extensions
Four Joomla-related additions in one week suggest attackers are scanning broadly across the extension ecosystem rather than focusing only on the core platform. -
AI development platforms entering normal vulnerability operations
Langflow belongs in the same inventory, logging, patching, and access-control processes as other enterprise applications. -
Shorter remediation timelines
Three-day KEV deadlines are becoming common for vulnerabilities that are exposed, actively exploited, and easy to automate.
Weekly Pulse
This week’s KEV additions focused on application functions that accept files, paths, or object identifiers and then act on them.
The Joomla cluster presents the clearest immediate risk because the flaws are unauthenticated and affect public-facing extensions. ColdFusion raises the potential impact by placing application infrastructure at risk, while Langflow shows that AI workflow platforms are now part of the same operational security landscape.
The practical lesson is straightforward: inventory the components beneath the main platform, patch quickly, and investigate whether exploitation happened before the fix was applied.
Bottom Line
Six exploited vulnerabilities entered the KEV catalog this week: four in Joomla extensions, one in Adobe ColdFusion, and one in Langflow.
The immediate priorities are to identify affected systems, apply the available fixes, remove unnecessary components, and search for signs of compromise.
When application features can write files, resolve paths, or execute workflows, they are part of the security perimeter.
Sources
- CISA — Known Exploited Vulnerabilities Catalog
- CISA — Three KEV Additions, July 7, 2026
- CISA — Adobe ColdFusion KEV Addition, July 7, 2026
- CISA — Two KEV Additions, July 10, 2026
- Adobe — ColdFusion Security Bulletin APSB26-68
- Langflow — CVE-2026-55255 Security Advisory
- NVD — CVE-2026-48908 JoomShaper SP Page Builder
- NVD — CVE-2026-56290 Joomlack Page Builder CK
- NVD — CVE-2026-48939 iCagenda
- NVD — CVE-2026-56291 Balbooa Forms
