

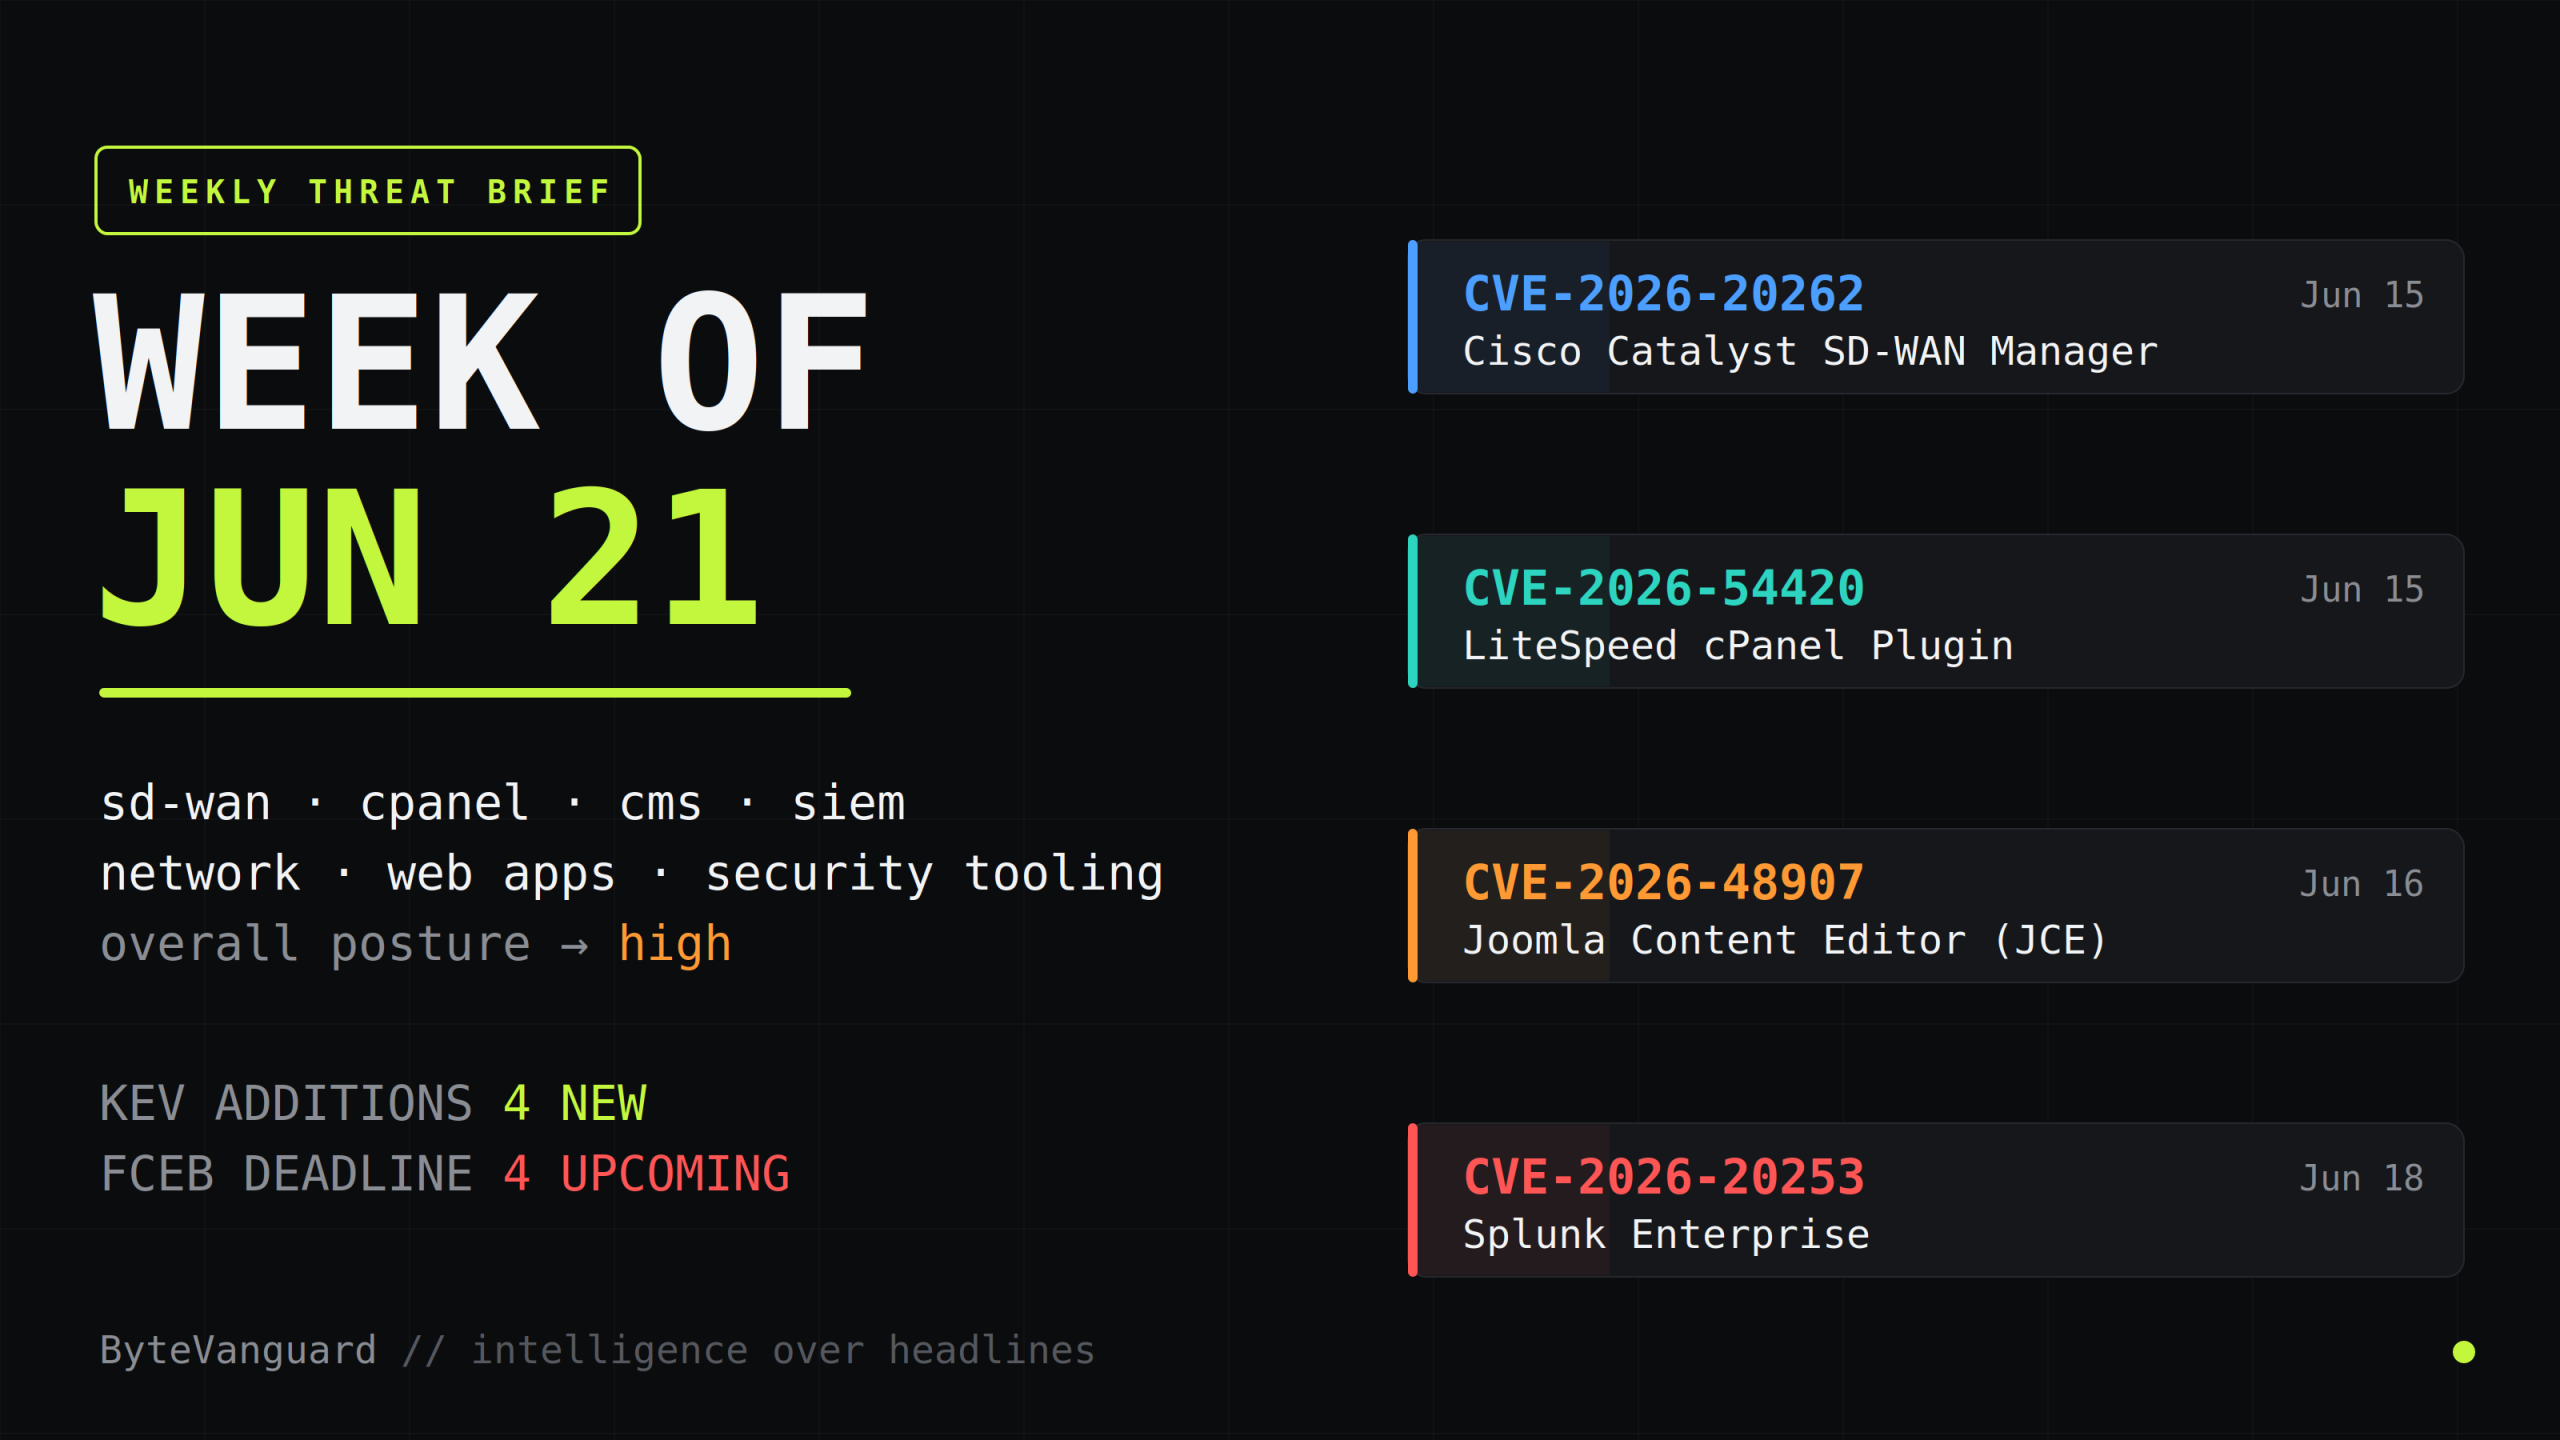
Week Ending: June 21, 2026 | Overall Risk Posture: High
The week ending June 21 was not defined by a large KEV surge. It was defined by the kind of systems CISA added to the Known Exploited Vulnerabilities catalog.
CISA added four vulnerabilities affecting Cisco Catalyst SD-WAN Manager, the LiteSpeed cPanel Plugin, the Joomla Content Editor extension, and Splunk Enterprise.
These products sit in very different environments: network management, shared hosting, content management, and security monitoring. But they share one important theme. Attackers continue to move toward trusted administrative and operational platforms — the systems defenders use to route networks, host websites, manage content, and monitor incidents.
This is why the week matters. The risk is not only that vulnerable software exists. The risk is what the vulnerable software is trusted to do.
Threat at a Glance
| Threat Area | Key Issue | Why It Matters | Defender Priority |
|---|---|---|---|
| SD-WAN Management | Cisco Catalyst SD-WAN Manager was added to KEV for CVE-2026-20262. | SD-WAN management systems sit close to routing, policy, configuration, and distributed network control. | Apply Cisco updates, restrict management access, and review administrative and file-write activity. |
| Shared Hosting | LiteSpeed cPanel Plugin was added for CVE-2026-54420. | Shared-hosting flaws can weaken tenant isolation and increase risk across multiple hosted sites. | Update LiteSpeed cPanel and WHM plugin components, review account activity, and check for file-system abuse. |
| CMS Extensions | Joomla Content Editor was added for CVE-2026-48907. | CMS editor extensions can become upload and execution paths on public-facing websites. | Update JCE, review editor profiles, inspect uploaded files, and check for unauthorized PHP content. |
| Security Monitoring | Splunk Enterprise was added for CVE-2026-20253. | Splunk often holds security telemetry, operational logs, alerts, dashboards, and investigation history. | Patch affected Splunk versions, restrict reachability, and validate telemetry integrity after remediation. |
Active Exploitation and Immediate Risk
-
Cisco Catalyst SD-WAN Manager kept control-plane risk in focus
CISA added CVE-2026-20262, affecting Cisco Catalyst SD-WAN Manager.
Cisco describes the issue as an arbitrary file write vulnerability in the web-based management interface, classed as a path traversal (CWE-22) and scored CVSS 6.5. To exploit it, an attacker needs valid credentials with at least write access — what Cisco characterizes as a low-privileged, single-task account. That requirement matters, but it does not make the vulnerability low-risk. Cisco found the flaw through internal security testing and has since confirmed limited, targeted exploitation in the wild. In real incidents, valid credentials are often obtained through phishing, password reuse, token theft, exposed admin accounts, or earlier compromise.
The bigger issue is the product role. SD-WAN Manager is not just another web application. It is part of the network control plane. It helps manage connectivity, policy, and routing behavior across distributed environments. A file-write vulnerability in that layer can become more serious than the same class of bug on a low-value internal server, because the written file can be used as a stepping stone to root.
Defenders should identify all Cisco Catalyst SD-WAN Manager deployments, apply Cisco’s fixed versions, restrict access to management interfaces, and review administrative activity before and after patching. File creation, file overwrite events, unexpected uploaded content, new administrative users, unusual API activity, and configuration changes should be treated as high-signal indicators. -
LiteSpeed cPanel Plugin showed why shared hosting remains a fragile trust layer
CISA added CVE-2026-54420, affecting the LiteSpeed cPanel Plugin.
The vulnerability affects LiteSpeed cPanel plugin versions before 2.4.8, as distributed in LiteSpeed WHM Plugin versions before 5.3.2.0, and is scored CVSS 8.5. The issue involves mishandling of symbolic links on shared-hosting servers running CloudLinux/CageFS, and it has been exploited in the wild since May 2026. The practical impact is privilege escalation to root: a user with only FTP or web shell access can escape CageFS isolation and take over the underlying host — and with it, every tenant on that shared server.
This matters because shared hosting depends on separation. One account should not be able to cross boundaries into another account, another customer’s files, or server-level resources. When a plugin weakens that boundary, the impact is not limited to a single website. The affected layer is part of the hosting control structure.
Hosting providers should confirm plugin versions, check whether vulnerable systems were exposed before patching, and review suspicious activity from cPanel users with FTP or web shell access. Customers using managed hosting should ask providers whether LiteSpeed cPanel and WHM plugin components were updated and whether any evidence of exploitation was observed. -
Joomla Content Editor turned a CMS extension into a code execution path
CISA added CVE-2026-48907, affecting the JCE editor extension for Joomla.
The vulnerability allows unauthenticated users to create new editor profiles, ultimately resulting in PHP code upload and execution. Scored CVSS 10.0, it requires no authentication and no user interaction. That combination makes it especially dangerous for public-facing Joomla sites, and it is already a mass-exploitation target: Joomla has warned that working exploit code is public and the attacks are automated, so even a site with no public registration is not safe.
JCE is not a small detail in the application stack. Editor extensions often control file handling, upload behavior, media paths, and user-facing content workflows. If that layer can be abused without authentication, an attacker may be able to move from public web access to server-side code execution.
The JCE project patched the underlying vulnerability in version 2.9.99.5 (June 3), added additional hardening in 2.9.99.6, and shipped 2.9.99.7 on June 18, which is the current secure release and also corrects an upload regression introduced in 2.9.99.6. Standardize on 2.9.99.7. Defenders should update immediately, review editor profiles, inspect upload directories, check temporary directories such as /tmp, and look for unexpected PHP files or modified configuration. -
Splunk Enterprise made the security platform itself the exposure layer
CISA added CVE-2026-20253, affecting Splunk Enterprise.
Splunk describes the issue as unauthenticated arbitrary file creation and truncation through a PostgreSQL sidecar service endpoint that lacks authentication controls. Splunk rates the vulnerability as critical with a CVSS score of 9.8. Affected Splunk Enterprise versions are 10.2 below 10.2.4 and 10.0 below 10.0.7, with fixes in 10.2.4, 10.0.7, and 10.4.0; only the 10.x release lines are listed as affected. The timeline is the part defenders should sit with: Splunk shipped the patch on June 10, a watchTowr proof-of-concept appeared on June 12, and Splunk confirmed exploitation on June 18 — a patch-to-exploitation window measured in days, on a platform that is itself a security control.
This is strategically important because Splunk often sits inside the security operations center. It may contain authentication logs, firewall events, endpoint telemetry, cloud audit trails, detection alerts, dashboards, analyst notes, and investigation history. A vulnerability in this system is not only an application risk. It can become a visibility risk.
Defenders should patch affected Splunk deployments quickly, restrict network reachability to Splunk services, and review whether any files were created, truncated, or modified during the exposure window. Teams should also confirm that log ingestion, alerting, dashboards, indexes, retention settings, and detection content were not disrupted.
Common Failure Patterns
-
Management systems are still treated like ordinary applications
Cisco Catalyst SD-WAN Manager shows why this is dangerous. A vulnerability in a management platform can affect more than the host where the bug exists. It can affect policy, routing, segmentation, and administrative control. -
Shared-hosting risk is often underestimated
LiteSpeed cPanel Plugin shows how a plugin flaw can matter beyond one user account. In shared-hosting environments, tenant isolation is the security model. Any weakness in that boundary deserves provider-level urgency. -
CMS extensions remain one of the easiest paths into public web infrastructure
Joomla JCE shows the recurring problem with plugins and extensions. They often sit close to file uploads, content workflows, and administrative behavior. When access control fails, exploitation can become simple and scalable. -
Security tools are not automatically secure because defenders use them
Splunk Enterprise is a reminder that monitoring platforms need the same hardening, patching, access control, and segmentation as any other high-value system. In some environments, they need more. -
Patching is often separated from compromise review
For all four KEV entries this week, updating software is necessary but not enough. If a system was reachable before remediation, defenders should also check whether it was abused before the patch was applied. -
Asset ownership slows response
SD-WAN may belong to network teams. Splunk may belong to security operations. cPanel may belong to hosting or platform teams. Joomla may belong to web or marketing teams. Attackers do not care which department owns the asset. Once exploitation is confirmed, ownership gaps become risk.
Defender Priorities
-
Patch Cisco Catalyst SD-WAN Manager and restrict management access
Apply Cisco’s fixed releases for CVE-2026-20262. Limit SD-WAN Manager access to trusted administrative networks, enforce strong authentication, review privileged users, and inspect logs for unusual file-write or configuration activity. -
Review SD-WAN Manager as a control-plane asset
Do not treat the affected system like a normal web server. Validate configuration integrity, administrative roles, API activity, unexpected uploads, and changes to network policy or routing behavior. -
Update LiteSpeed cPanel and WHM plugin components
Upgrade to LiteSpeed WHM Plugin v5.3.2.1 (bundled with cPanel user-end plugin v2.4.8) or later. Where an immediate update is not possible, removing the user-end plugin eliminates the attack surface as an interim step. Hosting providers should verify deployment across all affected shared-hosting servers. -
Investigate shared-hosting file-system anomalies
Look for unusual symlink behavior, unexpected file ownership, abnormal permission changes, suspicious activity from cPanel accounts, and signs that one account attempted to access files outside its expected boundary. -
Update Joomla Content Editor immediately
Move JCE to 2.9.99.7 (anything below 2.9.99.5 still carries the flaw). Review whether older Joomla sites, forgotten microsites, staging systems, or legacy public-facing deployments are still running vulnerable JCE versions. -
Inspect Joomla upload paths and editor profiles
Check for unauthorized editor profiles, unexpected PHP files, suspicious content in temporary directories, modified extension configuration, and web requests that attempted to upload or execute server-side code. -
Patch affected Splunk Enterprise versions
Upgrade Splunk Enterprise 10.2 deployments to 10.2.4 or later and 10.0 deployments to 10.0.7 or later, following Splunk’s advisory guidance. Confirm whether Splunk Cloud environments are already remediated through provider-side action. -
Validate Splunk telemetry integrity
Because this vulnerability affects a monitoring platform, defenders should confirm that logs were not truncated, collection was not interrupted, indexes were not modified, and alerts or dashboards were not unexpectedly changed. -
Use KEV as an incident-response trigger
For systems that were exposed before patching, ask whether there is evidence of compromise. KEV should trigger patching, but for high-value systems it should also trigger targeted investigation.
Signals to Watch
-
Control-plane exploitation remains a recurring enterprise theme
Cisco SD-WAN Manager continues the pattern of attackers and researchers focusing on systems that manage networks rather than only the endpoints inside them. This is the second Cisco SD-WAN Manager flaw added to KEV this month, which points to sustained interest in that management plane. -
Hosting infrastructure remains attractive because compromise can scale
LiteSpeed cPanel Plugin shows why shared-hosting platforms remain sensitive. A single weakness in hosting administration can affect many websites, users, or tenants. -
CMS plugins still create public-facing execution paths
Joomla JCE reinforces a simple reality: websites are often compromised through extensions, not the core CMS alone. Plugin inventory and update discipline remain essential. -
Security monitoring platforms are becoming more visible as targets
Splunk Enterprise shows why defenders need to harden the tools that store their evidence. A monitoring platform can become both a target and a blind spot. -
Authenticated vulnerabilities still matter when the asset is privileged
Cisco’s issue requires valid credentials, but that does not remove urgency. On management systems, credential theft plus file-write behavior can create meaningful attacker leverage. -
Patch status and compromise status are different questions
A system can be patched today and still have been abused yesterday. For KEV entries affecting management, hosting, CMS, or monitoring layers, defenders should answer both questions.
Weekly Pulse
The week ending June 21 showed exploitation pressure against trusted operational platforms rather than a single vulnerability class.
Cisco Catalyst SD-WAN Manager represented network control-plane risk. LiteSpeed cPanel Plugin represented shared-hosting and tenant-isolation risk. Joomla Content Editor represented CMS extension and file-upload risk. Splunk Enterprise represented security telemetry and monitoring-platform risk.
The common thread is trust. These systems are trusted to manage networks, host customer sites, edit public content, or collect security evidence. That trust is exactly why attackers care about them.
This week was not the loudest KEV week of 2026, but it was a meaningful one. The additions show that exploitation pressure continues to move toward systems that sit close to access, administration, visibility, and operational control.
Bottom Line
This week’s CISA KEV changes were not about one vendor or one exploit family. They were about trusted platforms becoming attack surfaces.
For defenders, the priority is clear: patch Cisco Catalyst SD-WAN Manager, update LiteSpeed cPanel and WHM plugin components, upgrade Joomla Content Editor, and remediate affected Splunk Enterprise deployments.
But the larger lesson is more important than the patch list. When a vulnerable product manages networks, hosts customer sites, controls uploads, or stores security telemetry, remediation should not stop at version control.
Defenders should ask what the vulnerable system could control, what it could expose, what logs it could alter, and what trust relationships it could affect.
The risk is not only what is vulnerable. The risk is what the vulnerable system is trusted to do.
Sources
- CISA — Known Exploited Vulnerabilities Catalog
- CISA — Adds Two Known Exploited Vulnerabilities to Catalog, June 15, 2026 (Cisco Catalyst SD-WAN Manager, LiteSpeed cPanel Plugin)
- CISA — Adds One Known Exploited Vulnerability to Catalog, June 16, 2026 (Joomla Content Editor)
- CISA — Adds One Known Exploited Vulnerability to Catalog, June 18, 2026 (Splunk Enterprise)
- Cisco — Catalyst SD-WAN Manager Arbitrary File Write Vulnerability (CVE-2026-20262)
- NVD — CVE-2026-20262 Cisco Catalyst SD-WAN Manager
- LiteSpeed — Security Update for LiteSpeed cPanel Plugin
- NVD — CVE-2026-54420 LiteSpeed cPanel Plugin
- CVE.org — CVE-2026-48907 Joomla Content Editor
- NVD — CVE-2026-48907 Joomla Content Editor
- Joomla Content Editor — JCE Security Update and a Free Patch for Older Sites
- Splunk — SVD-2026-0603 CVE-2026-20253 Advisory
- NVD — CVE-2026-20253 Splunk Enterprise
- CISA — BOD 26-04 Implementation Guidance: Prioritizing Security Updates Based on Risk
