CISA · KEV Alert
CISA Adds Four Known Exploited Vulnerabilities to Catalog (June 23, 2026) — the UniFi OS entries and BOD 26-04 remediation requirement


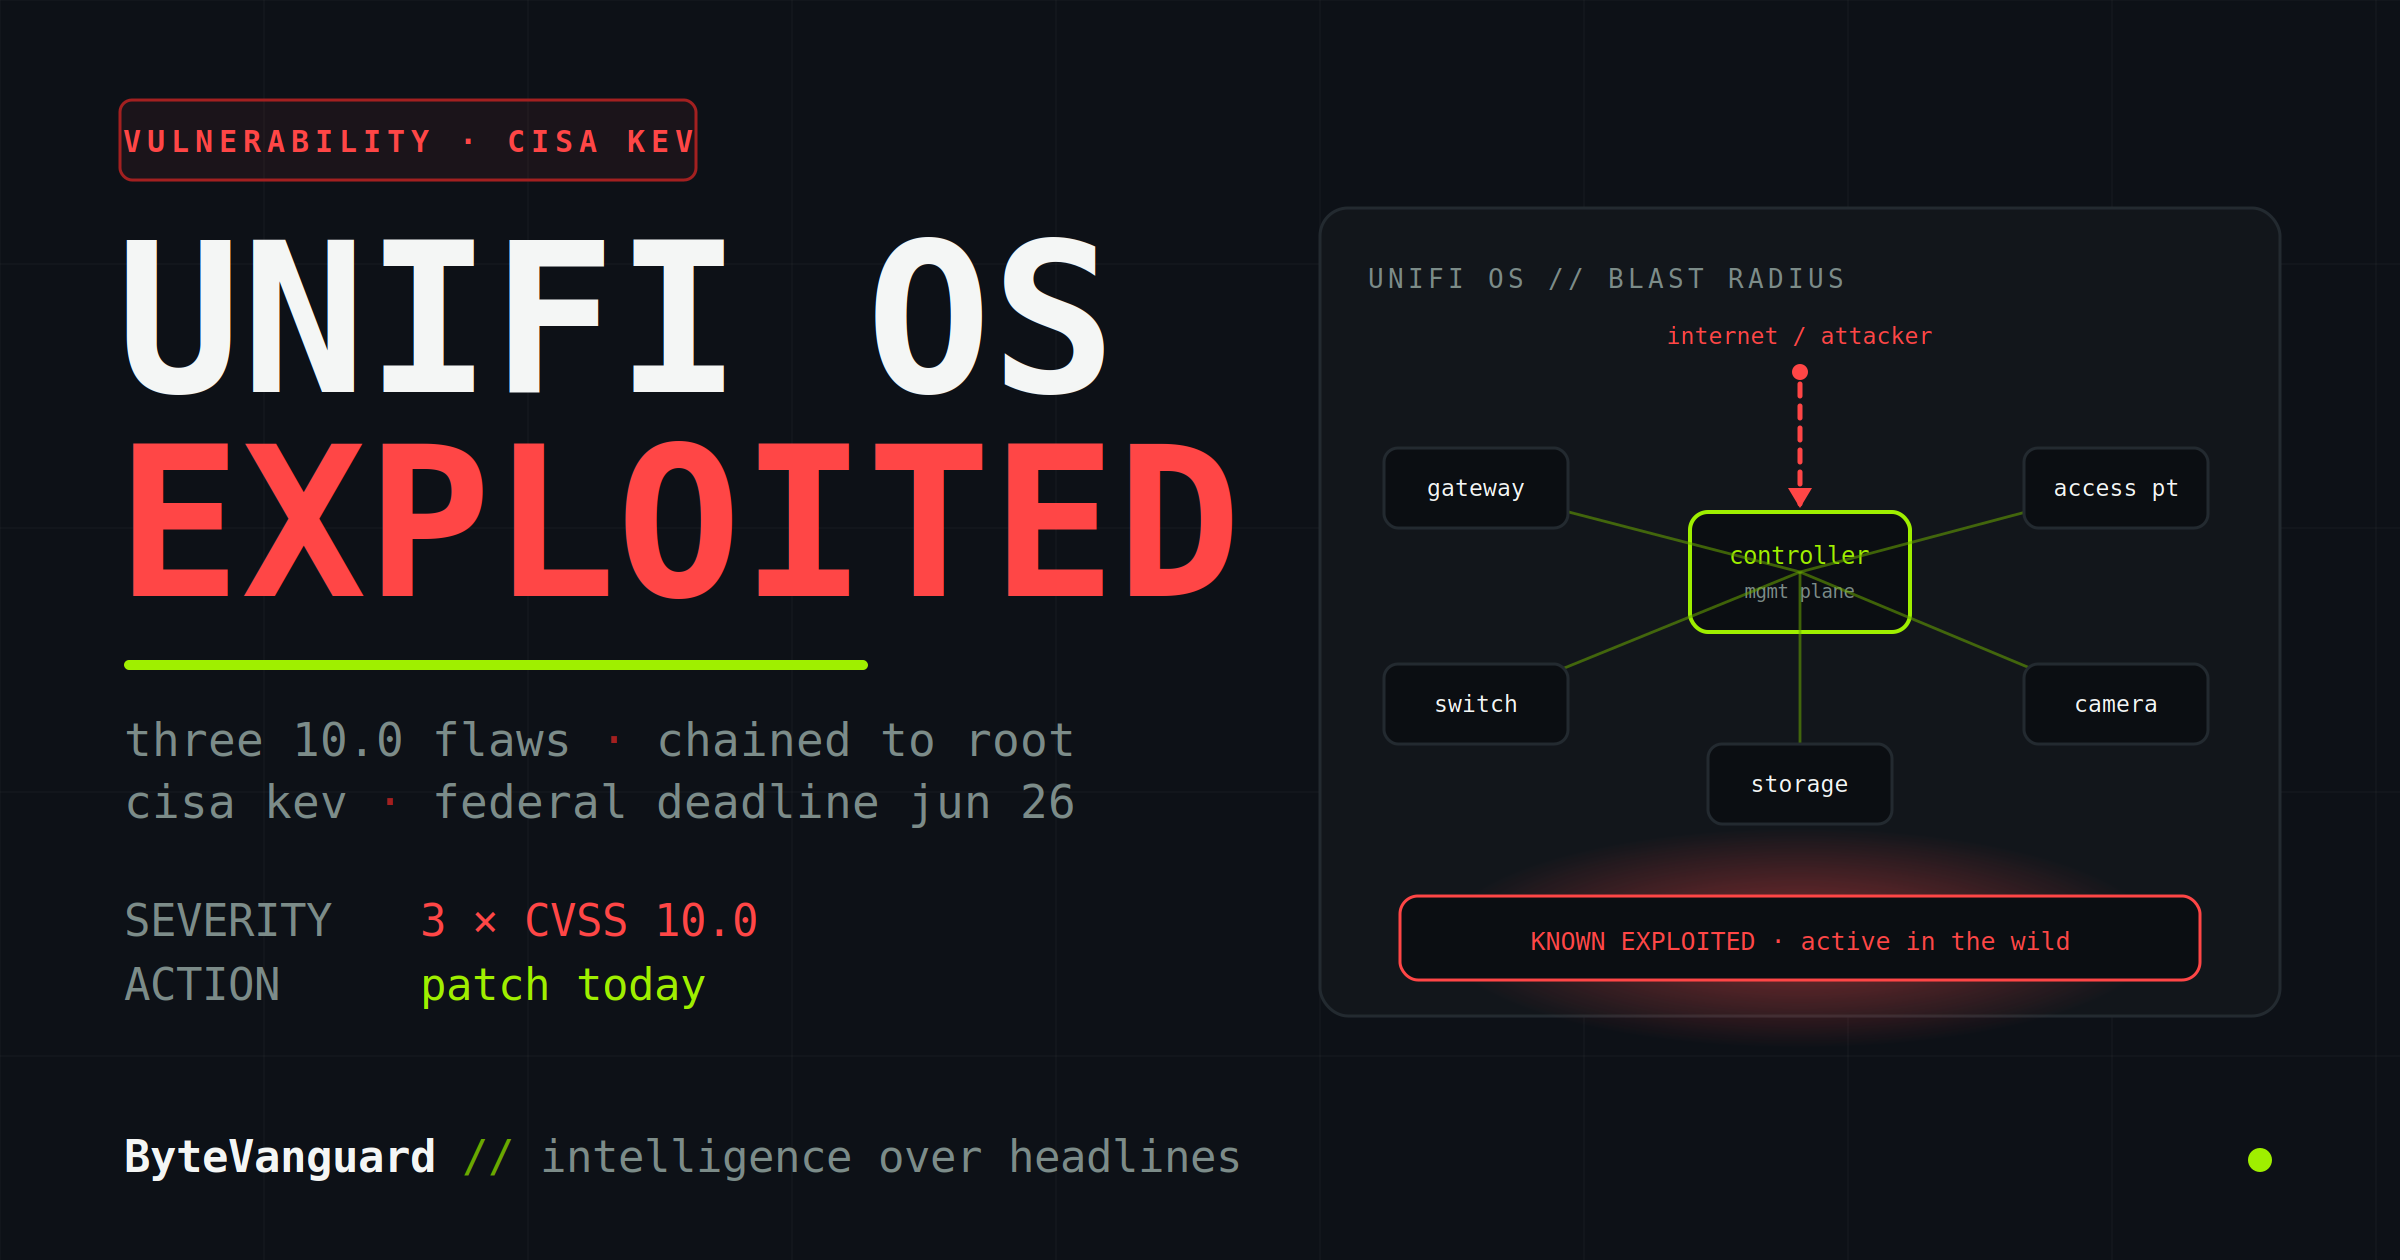
CISA just added three UniFi OS vulnerabilities to the Known Exploited Vulnerabilities catalog. The story is not only that Ubiquiti devices need patches. The bigger lesson is that the controller has become part of the perimeter — because whoever controls the controller may control the network behind it.
CISA added three Ubiquiti UniFi OS vulnerabilities to the Known Exploited Vulnerabilities catalog on June 23, 2026: CVE-2026-34908, CVE-2026-34909, and CVE-2026-34910. All three carry a CVSS 3.1 score of 10.0 from the CNA, and all three now sit in the category that matters most operationally: known exploited, not theoretical.
The federal remediation date is June 26, 2026. That three-day window is the point. Under CISA’s newer risk-based model, KEV is no longer treated like a slow patch queue. When exploitation is confirmed and the affected system has meaningful exposure or operational impact, defenders are expected to move fast.
For Ubiquiti customers, the immediate instruction is simple: update UniFi OS according to the vendor advisory. For defenders, the strategic lesson is larger: controllers, consoles, and management planes are now perimeter assets. They need to be inventoried, restricted, logged, and patched with the urgency normally reserved for VPNs, firewalls, and identity providers.
The KEV additions cover three weaknesses in UniFi OS: improper access control, path traversal, and improper input validation. Separately, each issue is serious. Chained together, security researchers showed they can become a root-level compromise path against affected UniFi OS Server instances.
| CVE | Issue | Why it matters |
|---|---|---|
| CVE-2026-34908 | Improper access control | Allows unauthorized changes to vulnerable UniFi OS systems when the attacker can reach the affected service. |
| CVE-2026-34909 | Path traversal | Allows access to files on the underlying operating system, creating a path toward account and system compromise. |
| CVE-2026-34910 | Improper input validation / command injection | Allows command injection on affected UniFi OS devices, completing the highest-impact part of the chain. |
Ubiquiti shipped fixes in Security Advisory Bulletin 064, releasing UniFi OS Server 5.0.8 in late May. CISA did not add the CVEs to KEV until June 23 — after exploitation was observed in the wild. That gap between a fix being available and consoles actually being patched is precisely the window attackers are working in.
Bishop Fox published proof-of-concept code and analysis showing how the three chain together. CVE-2026-34908 and CVE-2026-34909 form an authentication-gateway bypass rooted in how NGINX normalizes crafted requests: a request that begins with an auth-exempt prefix in its raw form resolves, once normalized, to a protected internal route. That bypass reaches an internal package-update function, where CVE-2026-34910 fails to validate package names — letting an attacker smuggle shell metacharacters into a command path and execute code as root. Bishop Fox validated the unauthenticated chain against a live UniFi OS Server 5.0.6 target. The flaws affect UniFi OS broadly — Server, hardware consoles, and Cloud Gateways — though the publicly demonstrated root chain targets Server builds.
The exploitation is not hypothetical. The vulnerability-tracking firm Defused reported attackers chaining the three flaws into remote code execution to distribute malware, and community reports during the activity described rogue administrator accounts named “John Sim” being created on exposed consoles during automated reconnaissance. Treat that as a reported indicator rather than confirmed campaign attribution — but it is a concrete artifact worth hunting for on any console that was reachable before patching.
This is the part defenders should not miss: the vulnerability label says UniFi OS, but the business impact is management-plane compromise. A controller is not a normal server. It is the place where network configuration, device identity, service state, and administrative authority converge.
For years, security teams thought of the perimeter as a physical or logical edge: firewalls, VPN concentrators, remote access portals, and internet-facing applications. That model still matters, but it no longer describes how modern infrastructure is actually controlled.
Today, many environments are governed by centralized platforms. A cloud console controls workloads. An identity provider controls access. An MDM platform controls devices. An RMM tool controls endpoints. A network controller controls gateways, switches, access points, cameras, and sometimes physical security systems.
That means the controller is no longer just an administrative convenience. It is a trust boundary. If an attacker reaches it, they may gain visibility into topology, configuration, administrative accounts, stored secrets, device relationships, network services, VPN settings, wireless networks, and management workflows.
This is why “we patched it” may not be a complete answer. Patching closes the known entry point. It does not automatically prove that no one entered before the patch. For exposed or broadly reachable controllers, defenders should treat this as a compromise-assessment event, not only a software-update event.
“A firewall protects the edge. A controller decides what the edge is allowed to do. That makes the controller a perimeter asset.”
There are plenty of critical vulnerabilities in networking gear. Some are noisy. Some are niche. Some require credentials, rare configurations, or unrealistic preconditions. This one deserves attention because it lands at the intersection of three uncomfortable realities.
The last point matters. UniFi deployments often live in the awkward space between consumer simplicity and enterprise importance. A small office may depend on it for Wi-Fi, routing, cameras, access, VPN, and remote administration. But the security governance around the controller may be closer to a home lab than a regulated enterprise system.
Attackers do not care how the device was purchased. If it is reachable, vulnerable, and privileged, it is infrastructure.
The risk is not limited to command execution on one Linux-based system. The controller may hold or influence multiple layers of the environment. That is what changes the defender response.
On a compromised controller, defenders should think beyond “remove the web shell” or “update the package.” A root-level compromise of a controller can expose stored secrets, signing keys, cloud tokens, TLS material, local databases, service credentials, VPN material, wireless configuration, RADIUS-related data, device adoption state, and administrative sessions.
It can also give the attacker a map. Controllers often know what devices exist, where they sit, how they connect, and which systems trust them. In a flat network or poorly segmented branch environment, that map can be more useful than a single stolen credential.
The fix starts with patching, but the response should not end with patching. The right approach is a short, disciplined containment and verification cycle.
Apply the fixed versions from Ubiquiti’s advisory. UniFi OS Server should be updated to 5.0.8 or later, and UniFi hardware consoles and Cloud Gateways should be updated according to the vendor’s product-specific guidance.
Do not leave controller interfaces broadly reachable. Restrict access to management networks, VPNs, identity-aware access paths, or tightly controlled administrative locations.
If the controller was reachable before patching, review it as a possible compromise. Look for new accounts, suspicious sessions, unexpected configuration changes, strange outbound traffic, and altered device state.
Controller compromise can expose signing keys, cloud tokens, TLS keys, database credentials, VPN material, Wi-Fi secrets, and other sensitive data. Rotate what the controller could read or use.
Place network controllers in restricted management segments. Limit which users and systems can reach them, and limit where the controller itself can initiate connections.
Send authentication, administrative, device, update, and configuration events to a central logging platform. A controller that is not logged is a blind spot with privileges.
The most important control is reachability. If the controller interface is reachable from too many places, every vulnerability becomes more dangerous. Patch speed matters, but exposure discipline is what decides whether the next controller bug becomes a crisis.
This incident should be uncomfortable for managed service providers, school districts, retail operators, small businesses, and distributed organizations. UniFi’s appeal is that it makes network management simple across sites. That same simplicity can blur ownership.
Who owns the controller? Who receives the advisory? Who approves the update? Who knows whether the management interface is exposed? Who checks whether a temporary port-forward from two years ago still exists? Who rotates the secrets if compromise is suspected?
Those questions matter because many UniFi deployments are operationally important but administratively informal. A branch may depend on the controller for connectivity, cameras, Wi-Fi, and remote access, while the controller itself is not treated like a critical security asset.
That gap is exactly where attackers live. They do not need a Fortune 500 perimeter if a branch controller gives them a foothold. They do not need a sophisticated cloud attack if an internet-reachable management plane gives them root.
Controller exploitation is often harder to see than normal endpoint compromise. There may be no obvious phishing email, no suspicious attachment, no noisy malware alert, and no user reporting that “something looked wrong.” If the attacker reaches the controller directly, the first visible sign may be a configuration change, a new account, an unusual outbound connection, or a device behaving differently.
That means defenders should search for sequences, not just single indicators. A new admin account followed by a configuration export. A controller update followed by an unexpected outbound connection. A new device adoption event from the wrong network. A change to firewall, VPN, wireless, or camera settings without an approved ticket.
That is why controller logs need to be retained and centralized. If logs stay only on the device, a root-level attacker may be able to tamper with the evidence. Central logging does not prevent compromise, but it gives defenders a second copy of the story.
The UniFi OS KEV additions are part of a larger pattern. Attackers increasingly target systems that manage other systems: VPN appliances, RMM tools, hypervisors, identity providers, cloud consoles, CI/CD systems, firewalls, and controllers. These platforms sit close to the trust fabric. They are valuable because they provide leverage.
That is why vulnerability management needs a category above “critical server.” Some assets deserve accelerated handling because of what they control. A low-population controller that governs many devices may be more urgent than a larger fleet of ordinary endpoints.
The practical rule is simple: if a system can change the network, change identity, deploy code, manage devices, or issue trust, it belongs in the highest-priority patch and monitoring tier.
CISA’s UniFi OS KEV additions are not just a Ubiquiti story. They are a reminder that the perimeter has shifted upward into the systems that manage infrastructure. Firewalls still matter. VPNs still matter. But controllers now sit beside them as high-value control points.
The immediate response is clear: patch UniFi OS, remove unnecessary exposure, review logs, rotate secrets where needed, and investigate exposed pre-patch controllers. The long-term response is harder but more important: stop treating management planes like back-office tools.
Sourcing: vulnerability details and mitigation guidance are drawn from Ubiquiti Security Advisory Bulletin 064, CISA’s June 23 KEV alert and catalog, NVD CVE records, Bishop Fox’s UniFi OS Server analysis, and reporting from BleepingComputer and SecurityWeek. Bishop Fox validated the unauthenticated chain on UniFi OS Server 5.0.6; the fix shipped in UniFi OS Server 5.0.8, and organizations should check Ubiquiti’s advisory for exact product-specific fixed versions on consoles and Cloud Gateways. Reports of in-the-wild exploitation — including rogue “John Sim” administrator accounts — come from the vulnerability-tracking firm Defused and community telemetry, and should be treated as reported indicators rather than confirmed attribution.
If you find ByteVanguard useful, you can support the site and help keep the analysis independent.
Support the analysis