FIRST · EPSS FAQ
Defines the EPSS score as a 30-day probability of exploitation activity, refreshed daily, with percentile as relative rank


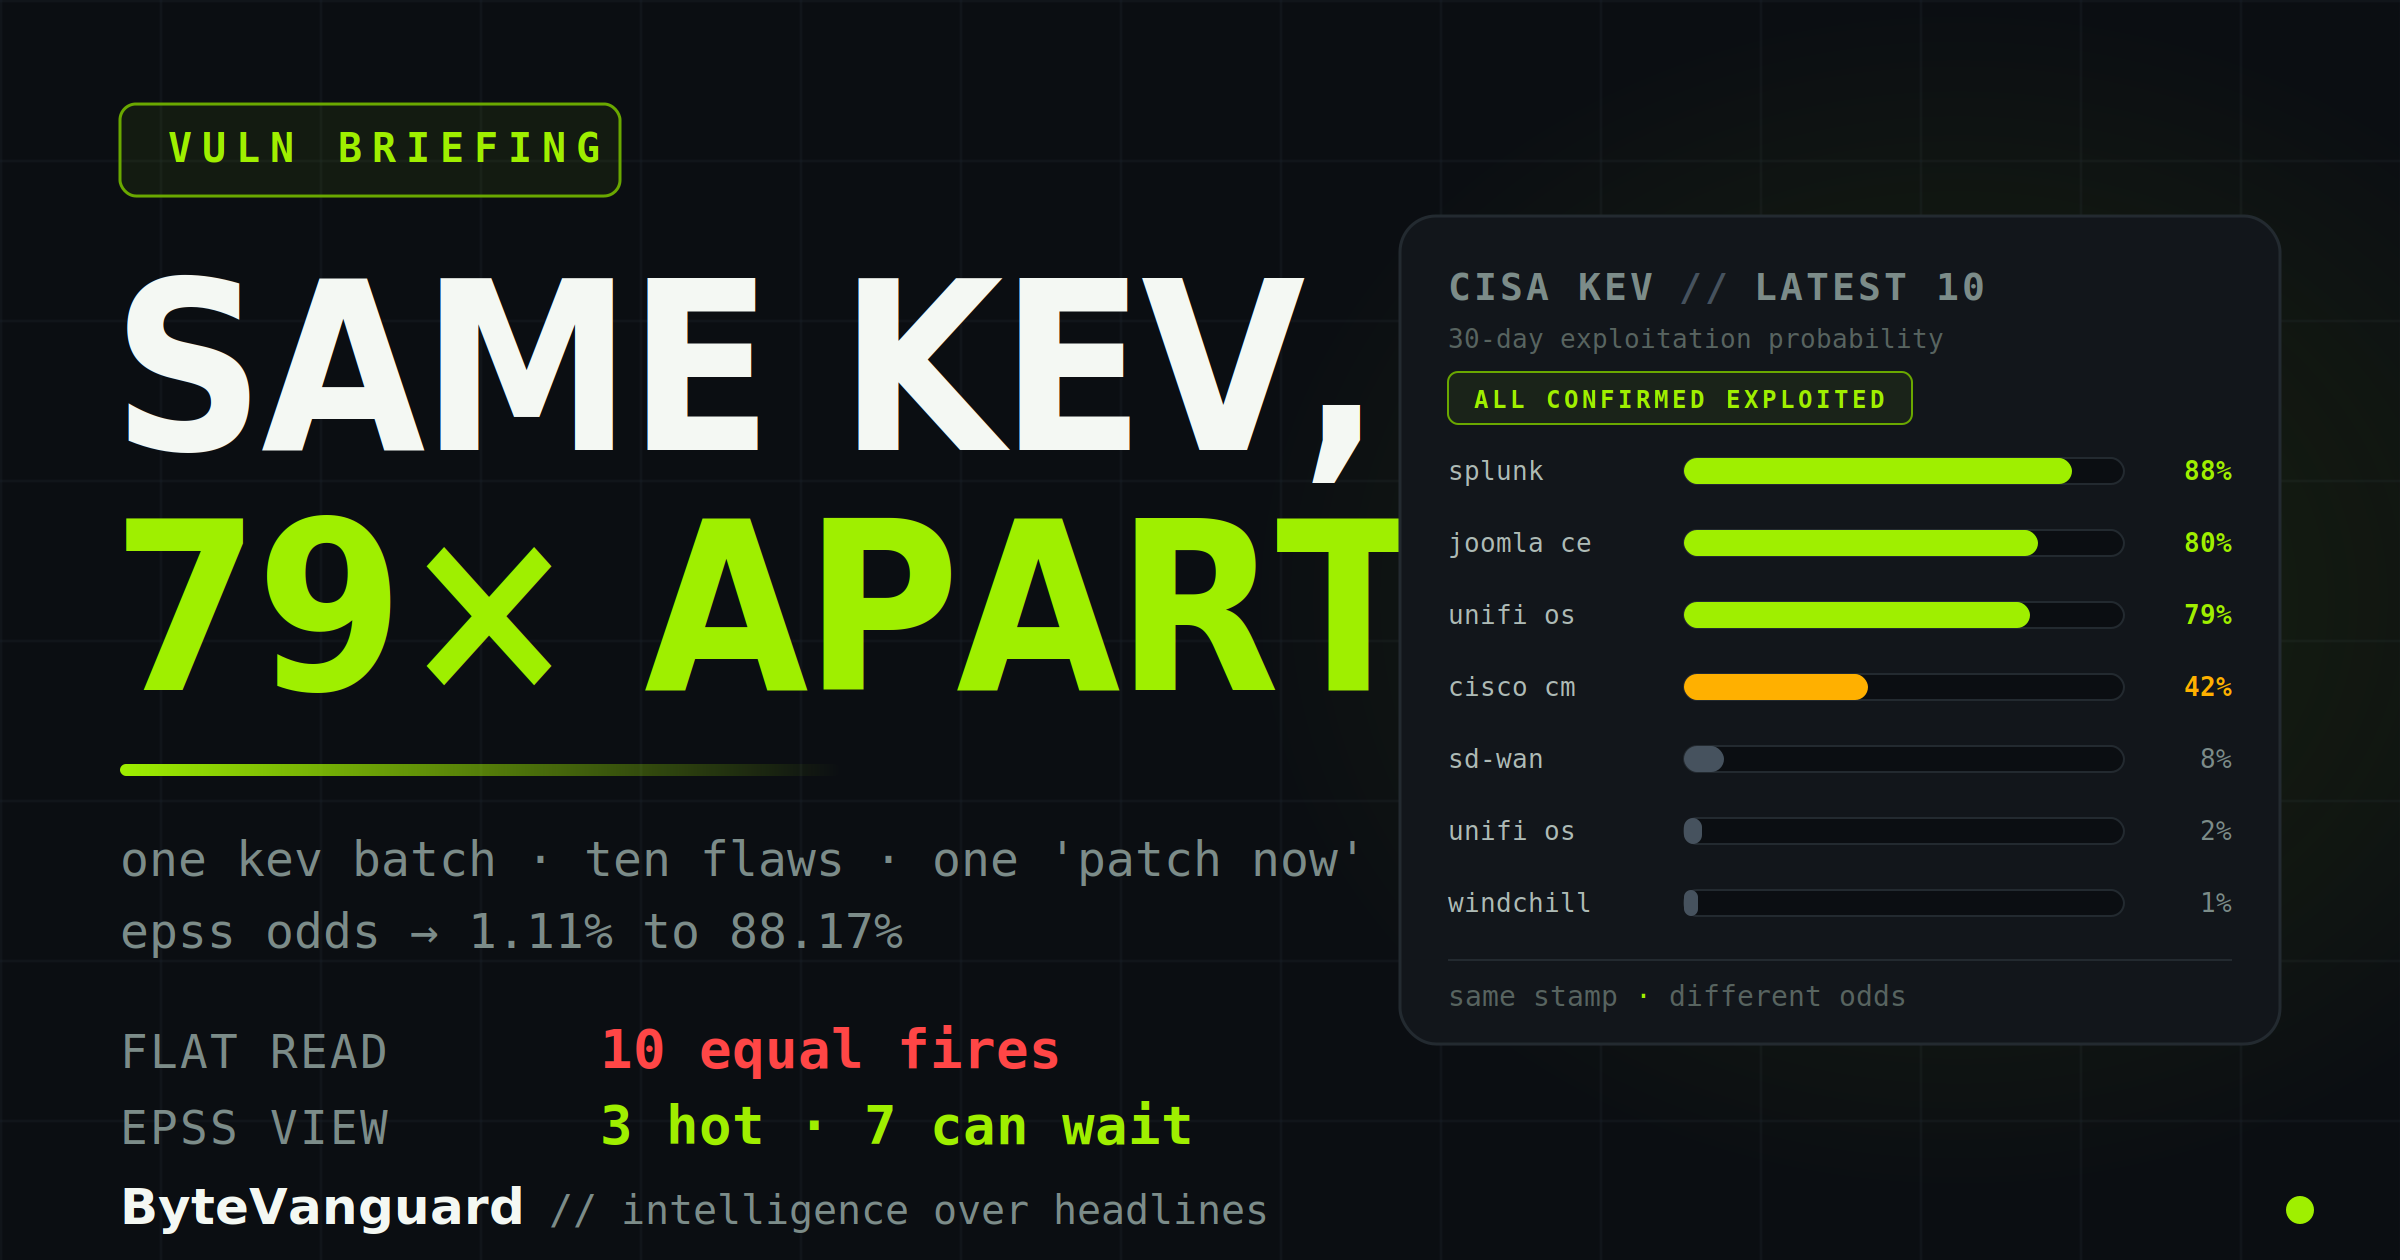
Two flaws can share the same catalog, the same date, and the same “patch now” stamp — and be eighty times apart on whether either is actually being hit. CISA’s KEV tells you what’s exploited. It has no way to tell you what’s urgent. EPSS does.
On June 25, CISA added two vulnerabilities to the Known Exploited Vulnerabilities catalog on the same day: an input-validation flaw in PTC Windchill and a server-side request forgery bug in Cisco Unified Communications Manager. Read flatly — the way most backlogs read KEV — they carry identical instructions: confirmed exploited, remediate now.
Read against EPSS, they are not in the same universe. The Windchill flaw carries a 30-day exploitation probability of 1.11%. The Cisco SSRF carries 41.69%, and lands in the 98th percentile of every scored CVE in the world. Same catalog, same day, same federal mandate — roughly forty times the near-term pressure. And that’s not even the widest gap in the batch.
This is the last ten entries on our KEV tracker, sorted by EPSS. Every one of them is flagged identically by the catalog. The third column is the one the catalog can’t see.
| Vulnerability | KEV added | EPSS (30-day) | Percentile |
|---|---|---|---|
| CVE-2026-20253 · Splunk Enterprise (missing auth) | Jun 18 | 88.17% | 99.75 |
| CVE-2026-48907 · Joomla Content Editor | Jun 16 | 80.43% | 99.57 |
| CVE-2026-34910 · UniFi OS — input validation (10.0) | Jun 23 | 78.56% | 99.53 |
| CVE-2026-20230 · Cisco Unified CM — SSRF | Jun 25 | 41.69% | 98.51 |
| CVE-2026-20262 · Cisco Catalyst SD-WAN Mgr | Jun 15 | 7.68% | 93.84 |
| CVE-2026-34908 · UniFi OS — access control (10.0) | Jun 23 | 2.45% | 82.36 |
| CVE-2026-34909 · UniFi OS — path traversal (10.0) | Jun 23 | 2.27% | 80.85 |
| CVE-2026-54420 · LiteSpeed cPanel plugin | Jun 15 | 1.26% | 65.95 |
| CVE-2025-67038 · Lantronix EDS5000 | Jun 23 | 1.13% | 62.38 |
| CVE-2026-12569 · PTC Windchill / FlexPLM | Jun 25 | 1.11% | 61.71 |
Three entries under genuine, near-term assault. One in between. Six sitting in the statistical long grass. A flat reading sees ten equal fires; the data sees a distribution. The catalog tells you what to care about. It does not tell you what to do first.
The confusion comes from treating KEV and EPSS as if they answer the same thing. They don’t.
KEV is binary and retrospective. A CVE is in the catalog or it isn’t. Inclusion means exploitation was observed at least once, somewhere — that’s the whole bar. It is a membership test, not a ranking, and it says nothing about how much pressure a flaw is under right now.
EPSS is continuous and forward-looking. It publishes a probability that a given CVE will see exploitation activity in the next 30 days, refreshed daily, alongside a percentile that places it against every other scored vulnerability. It says nothing about whether exploitation has already happened — only what’s likely next.
So the two are complementary, not redundant. KEV confirms; EPSS forecasts. The error that wrecks a backlog is using the membership test as the priority list. Being in the room is not the same as being first in line.
If you wanted a controlled test of this, you couldn’t do better than the three UniFi OS flaws CISA added on June 23. We covered them when they landed: all three rated CVSS 10.0, all three confirmed exploited, all added the same day. On every axis a flat backlog can see, they are identical triplets.
EPSS pulls them apart. The input-validation flaw, CVE-2026-34910, sits at 78.56% — top of the catalog. The path-traversal and access-control flaws beside it sit at 2.27% and 2.45%. Same vendor, same severity, same KEV date, and a thirty-fold gap in near-term exploitation likelihood. Given one maintenance window this week, that’s which of the three to spend it on — while the other two stay on the list for their turn.
“CVSS said 10.0. KEV said exploited. Both were true. Neither told you where to start.“
Before you reorganize anything around EPSS, internalize the one place it misleads people. Look back at the Windchill flaw: probability 1.11%, but percentile 61.71. That reads like a contradiction — how is a one-percent chance ranked above three-fifths of all CVEs?
This would be academic if volume were manageable. It isn’t. 2025 closed with 48,185 published CVEs — about 130 a day, weekends included. Nobody patches that. KEV is the community’s best coarse filter against the flood: roughly 1,629 active entries, a rounding error against the total, and a defensible “care about these” list.
But the filter still hands you sixteen hundred line items stamped “exploited, patch now,” and a flat reading collapses them into one undifferentiated emergency. KEV is also conservative on the front end — VulnCheck counted 883 CVEs newly exploited in 2025 against CISA’s 245 catalog additions. KEV is a floor on what’s confirmed, not a forecast of what’s coming. EPSS is the layer that restores the gradient the catalog flattens.
None of this is an argument to ignore low-EPSS entries. It’s an argument to stop treating the list as flat. Two moves and one adjustment:
KEV inclusion means confirmed exploitation — the question of whether is settled. A 1.11% flaw stays on the list. Low EPSS is “later,” never “never.”
Probability first, percentile for context. The high-band items — Splunk at 88%, UniFi’s input-validation flaw at 79% — take your nearest windows. The tail waits its turn.
EPSS is environment-agnostic. An internet-facing asset at a mid-band score can outrank an internal one at the top. EPSS sets the global order; your inventory edits it locally.
Scores move. Today’s 2% becomes next week’s 60% the moment a working exploit drops. Sequence off live data — never cache a one-time read.
We made the structural version of this case in our BOD 26-04 analysis: the flat, one-size deadline was always the wrong shape for a catalog this varied. Applied to this week, the model sorts the ten entries into four bands:
Your KEV backlog isn’t lying about what’s exploited. The catalog is honest, and it’s right. It’s lying about what’s urgent — because it has no way to say. Keep the floor: patch all of it. But stop pretending a 1.11% flaw and an 88.17% flaw, stamped on the same line by the same list on the same day, are the same emergency.
Sourcing: all EPSS values and KEV dates are drawn from ByteVanguard’s KEV + EPSS tracker (EPSS snapshot 2026-06-28). EPSS methodology — a 30-day probability of exploitation activity, with percentile as relative rank — follows FIRST’s published definition. The 2025 CVE-volume figure is from Jerry Gamblin’s 2025 CVE Data Review; the 883-vs-245 exploitation gap is VulnCheck data. UniFi CVSS 10.0 ratings per our prior coverage. EPSS is environment-agnostic and does not reflect any single organization’s exposure.
If you find ByteVanguard useful, you can support the site and help keep the analysis independent.
Support the analysis