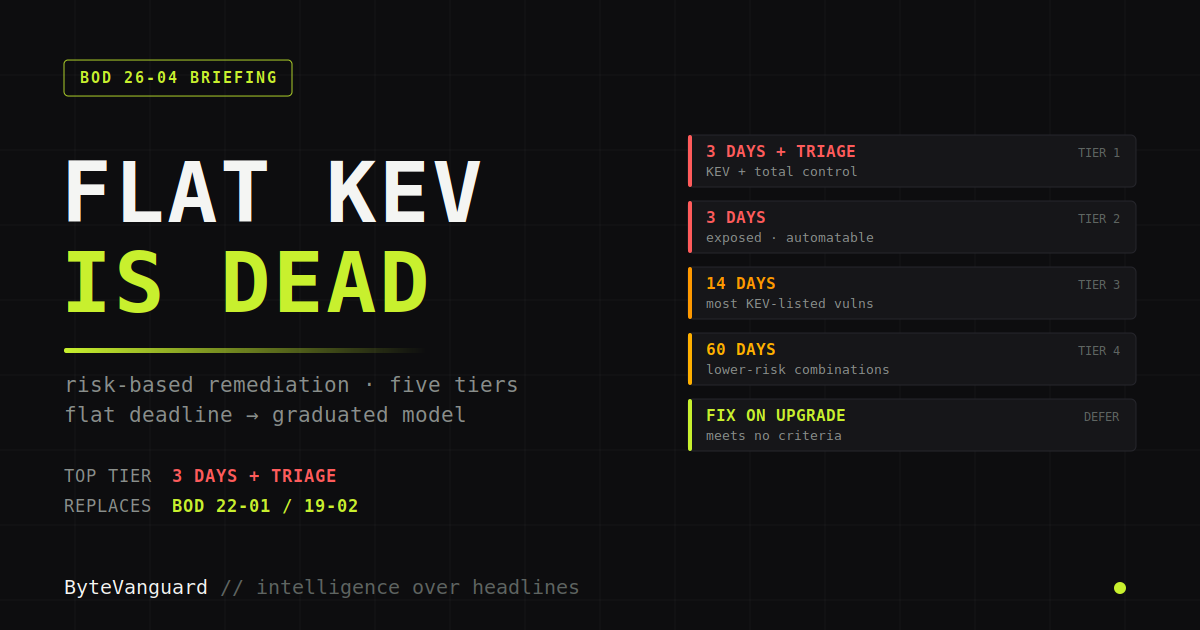
Briefings On June 10, CISA retired the directive that shaped a decade of vulnerability management. BOD 26-04 replaces the flat “every KEV on the same clock” rule with [...]
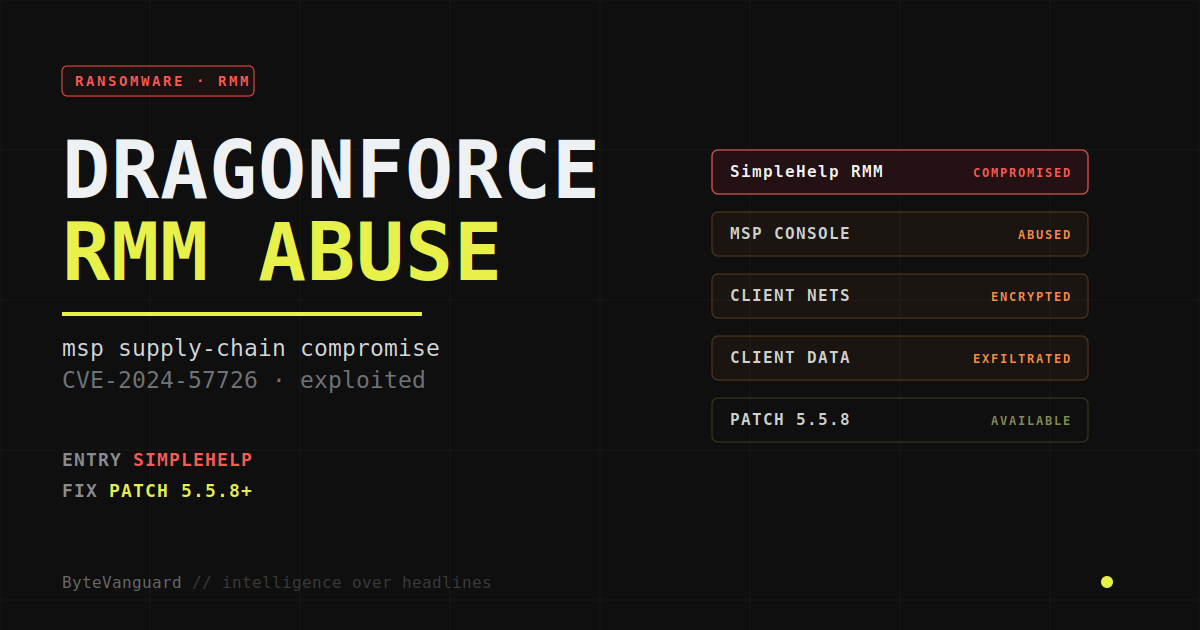
One RMM, 200 Victims: How DragonForce Scales Ransomware | ByteVanguard Ransomware DragonForce doesn’t attack organizations one at a time. It finds the IT management software that sits above [...]
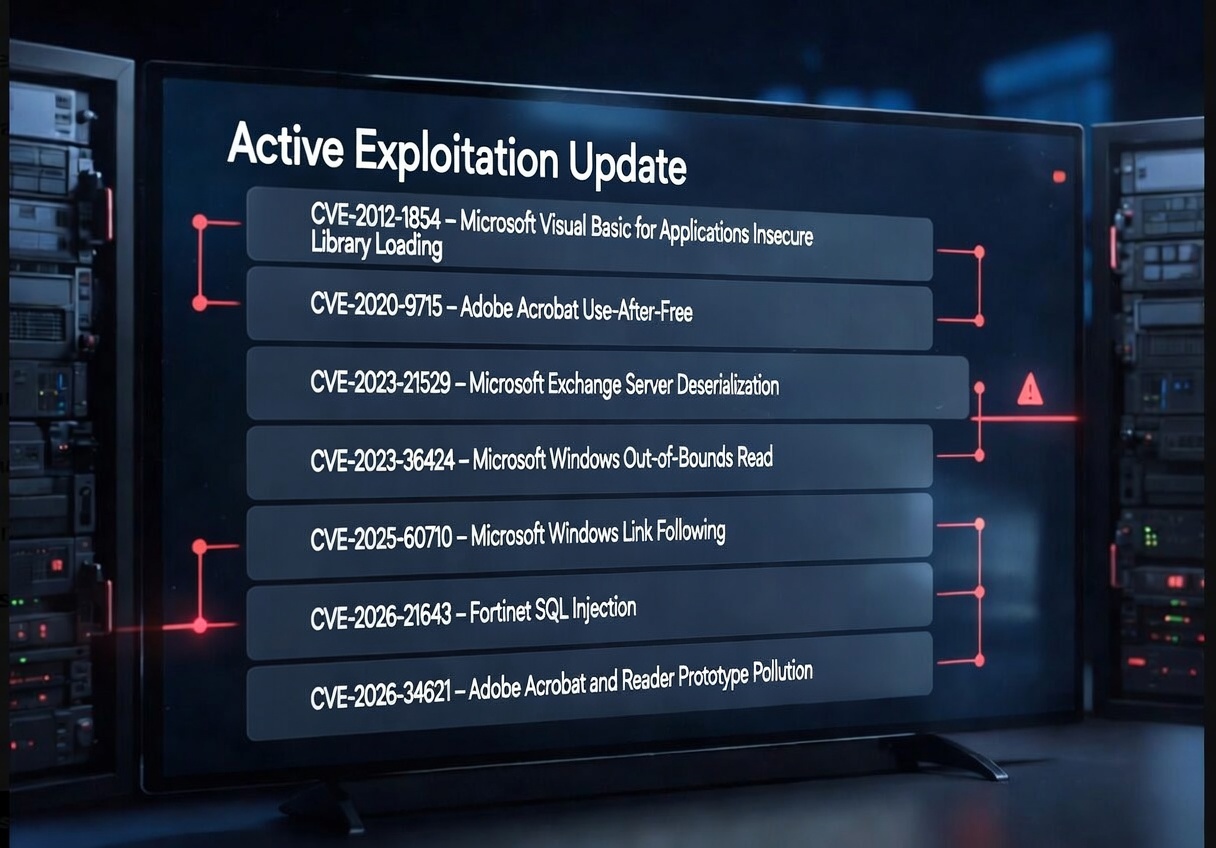
Published: April 14, 2026 CISA KEV Update: On April 13, CISA added seven new vulnerabilities to its Known Exploited Vulnerabilities catalog. On paper, the list looks strange: a [...]