Published: February 19, 2026 Executive Summary Multi-modal jailbreaking represents a significant evolution in AI model abuse: shifting from text-only prompt injection to cross-modal attacks that embed hidden instructions [...]
The Threat at a Glance Threat Type Insider-Enabled Data Exfiltration via Unauthorized AI Deployments (Shadow AI / Rogue LLMs) Severity High (Widespread Adoption, Persistent Internal Risk, High Impact [...]
The Threat at a Glance Threat Type Social Engineering + Real-Time AiTM Phishing (Vishing-as-a-Service) Severity High (Effective Bypass of MFA/SSO – Comparable CVSS ~8.2) Affected Systems SSO Providers [...]
In the fast-paced arena of agentic AI, where open-source tools promise to bridge large language models with real-world actions, Clawdbot (rebranded amid controversy to Moltbot and then OpenClaw) [...]
Voice-phishing (vishing) toolkits are rapidly proliferating across dark web forums, Telegram channels, and underground cybercrime marketplaces in early 2026. These customizable kits empower even novice attackers to launch [...]
In the rapidly expanding world of agentic AI tooling, the Model Context Protocol (MCP) has become a cornerstone for enabling large language models like Claude to interact with [...]
A sophisticated malware campaign known as GhostPoster has expanded significantly, with security researchers uncovering 17 additional malicious browser extensions across Chrome, Edge, and Firefox stores. These extensions, which [...]
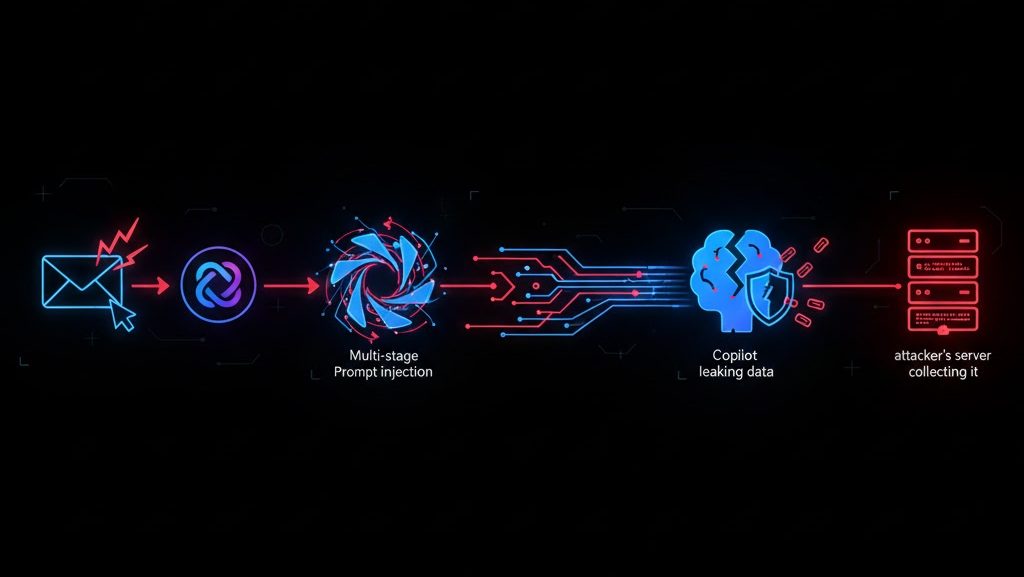
A new attack technique called Reprompt allows malicious actors to hijack active Microsoft Copilot sessions and trick the AI into leaking sensitive user data, according to researchers at [...]