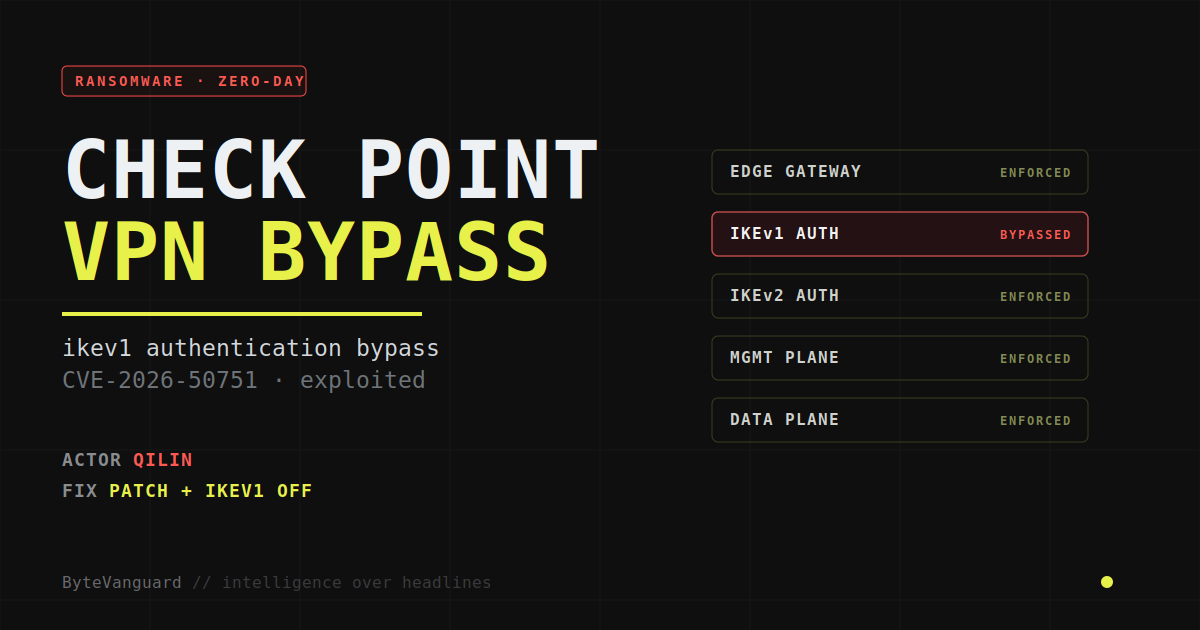
Ransomware The most prolific ransomware operation of 2026 didn’t need new malware to break into Check Point’s customers. It needed one logic flaw in a VPN protocol that [...]
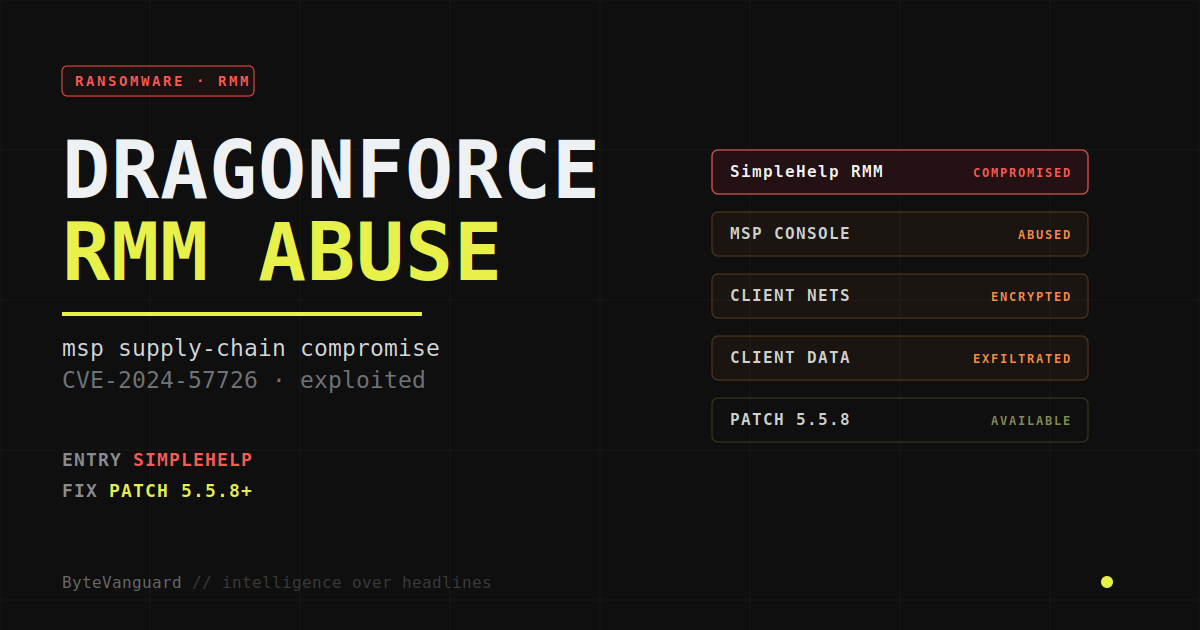
One RMM, 200 Victims: How DragonForce Scales Ransomware | ByteVanguard Ransomware DragonForce doesn’t attack organizations one at a time. It finds the IT management software that sits above [...]
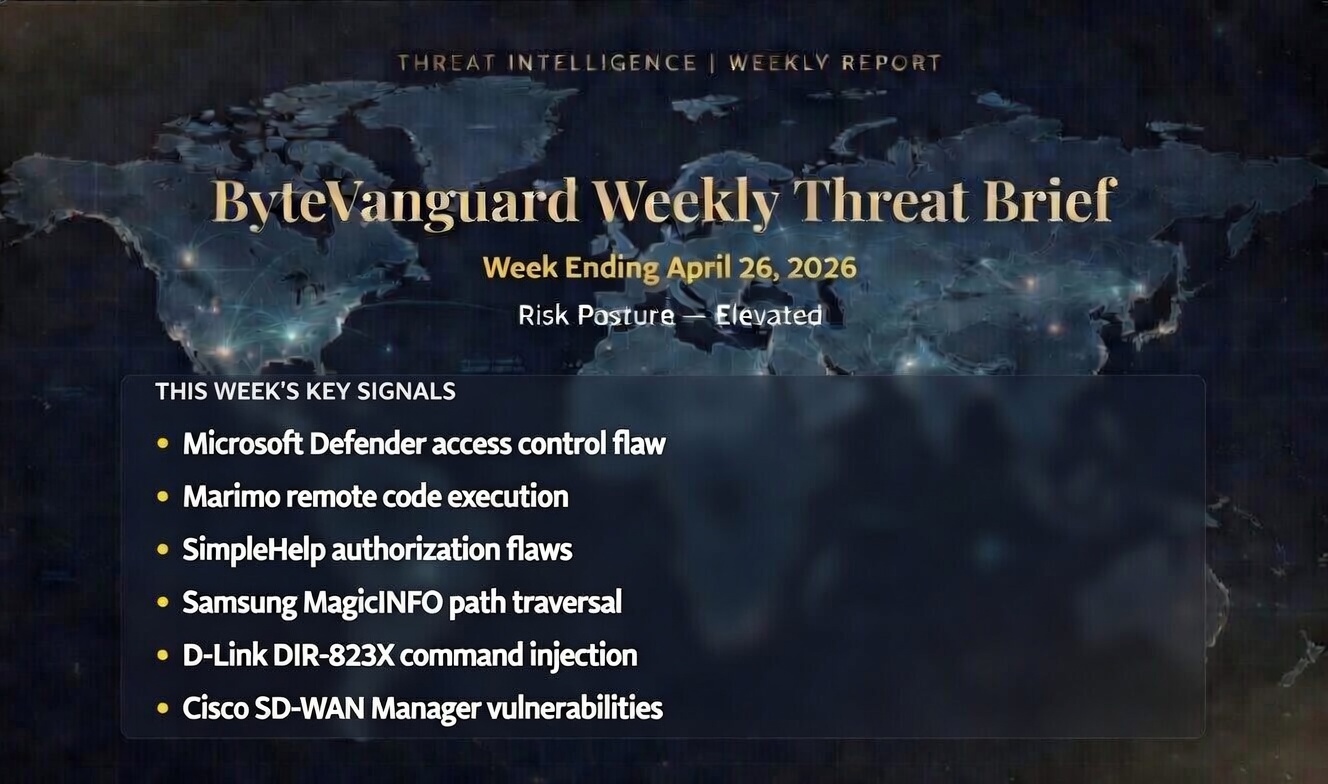
Weekly Threat Brief — Week Ending April 26, 2026 | ByteVanguard Published: April 27, 2026 Overall Risk Posture: Elevated The week ending April 26 was defined by exploited [...]
The 30-Minute Breakout: How Edge Exploits Compress Ransomware Timelines Published: March 4, 2026 | ByteVanguard Executive Summary Breakout time—not dwell time—defines modern ransomware operations. Ransomware breakout time has [...]
Executive Overview Identity compromise is no longer a supporting tactic in Microsoft 365 intrusions — it is the primary entry point. By early 2026, Microsoft reports processing approximately [...]
The Threat at a Glance Threat Type Defense Evasion via EDR / Sysmon Disruption Severity High (Critical for Detection & Response; Enables Ransomware & APT Persistence – Comparable [...]
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) concluded 2025 with its Known Exploited Vulnerabilities (KEV) Catalog reaching 1,484 entries, reflecting a nearly 20% increase from the 1,239 [...]
ZeroFox Intelligence released its 2026 cyber threat predictions on December 16, 2025, highlighting generative AI’s full integration into attacks, geopolitical influences on cybercrime, and persistent ransomware trends based [...]