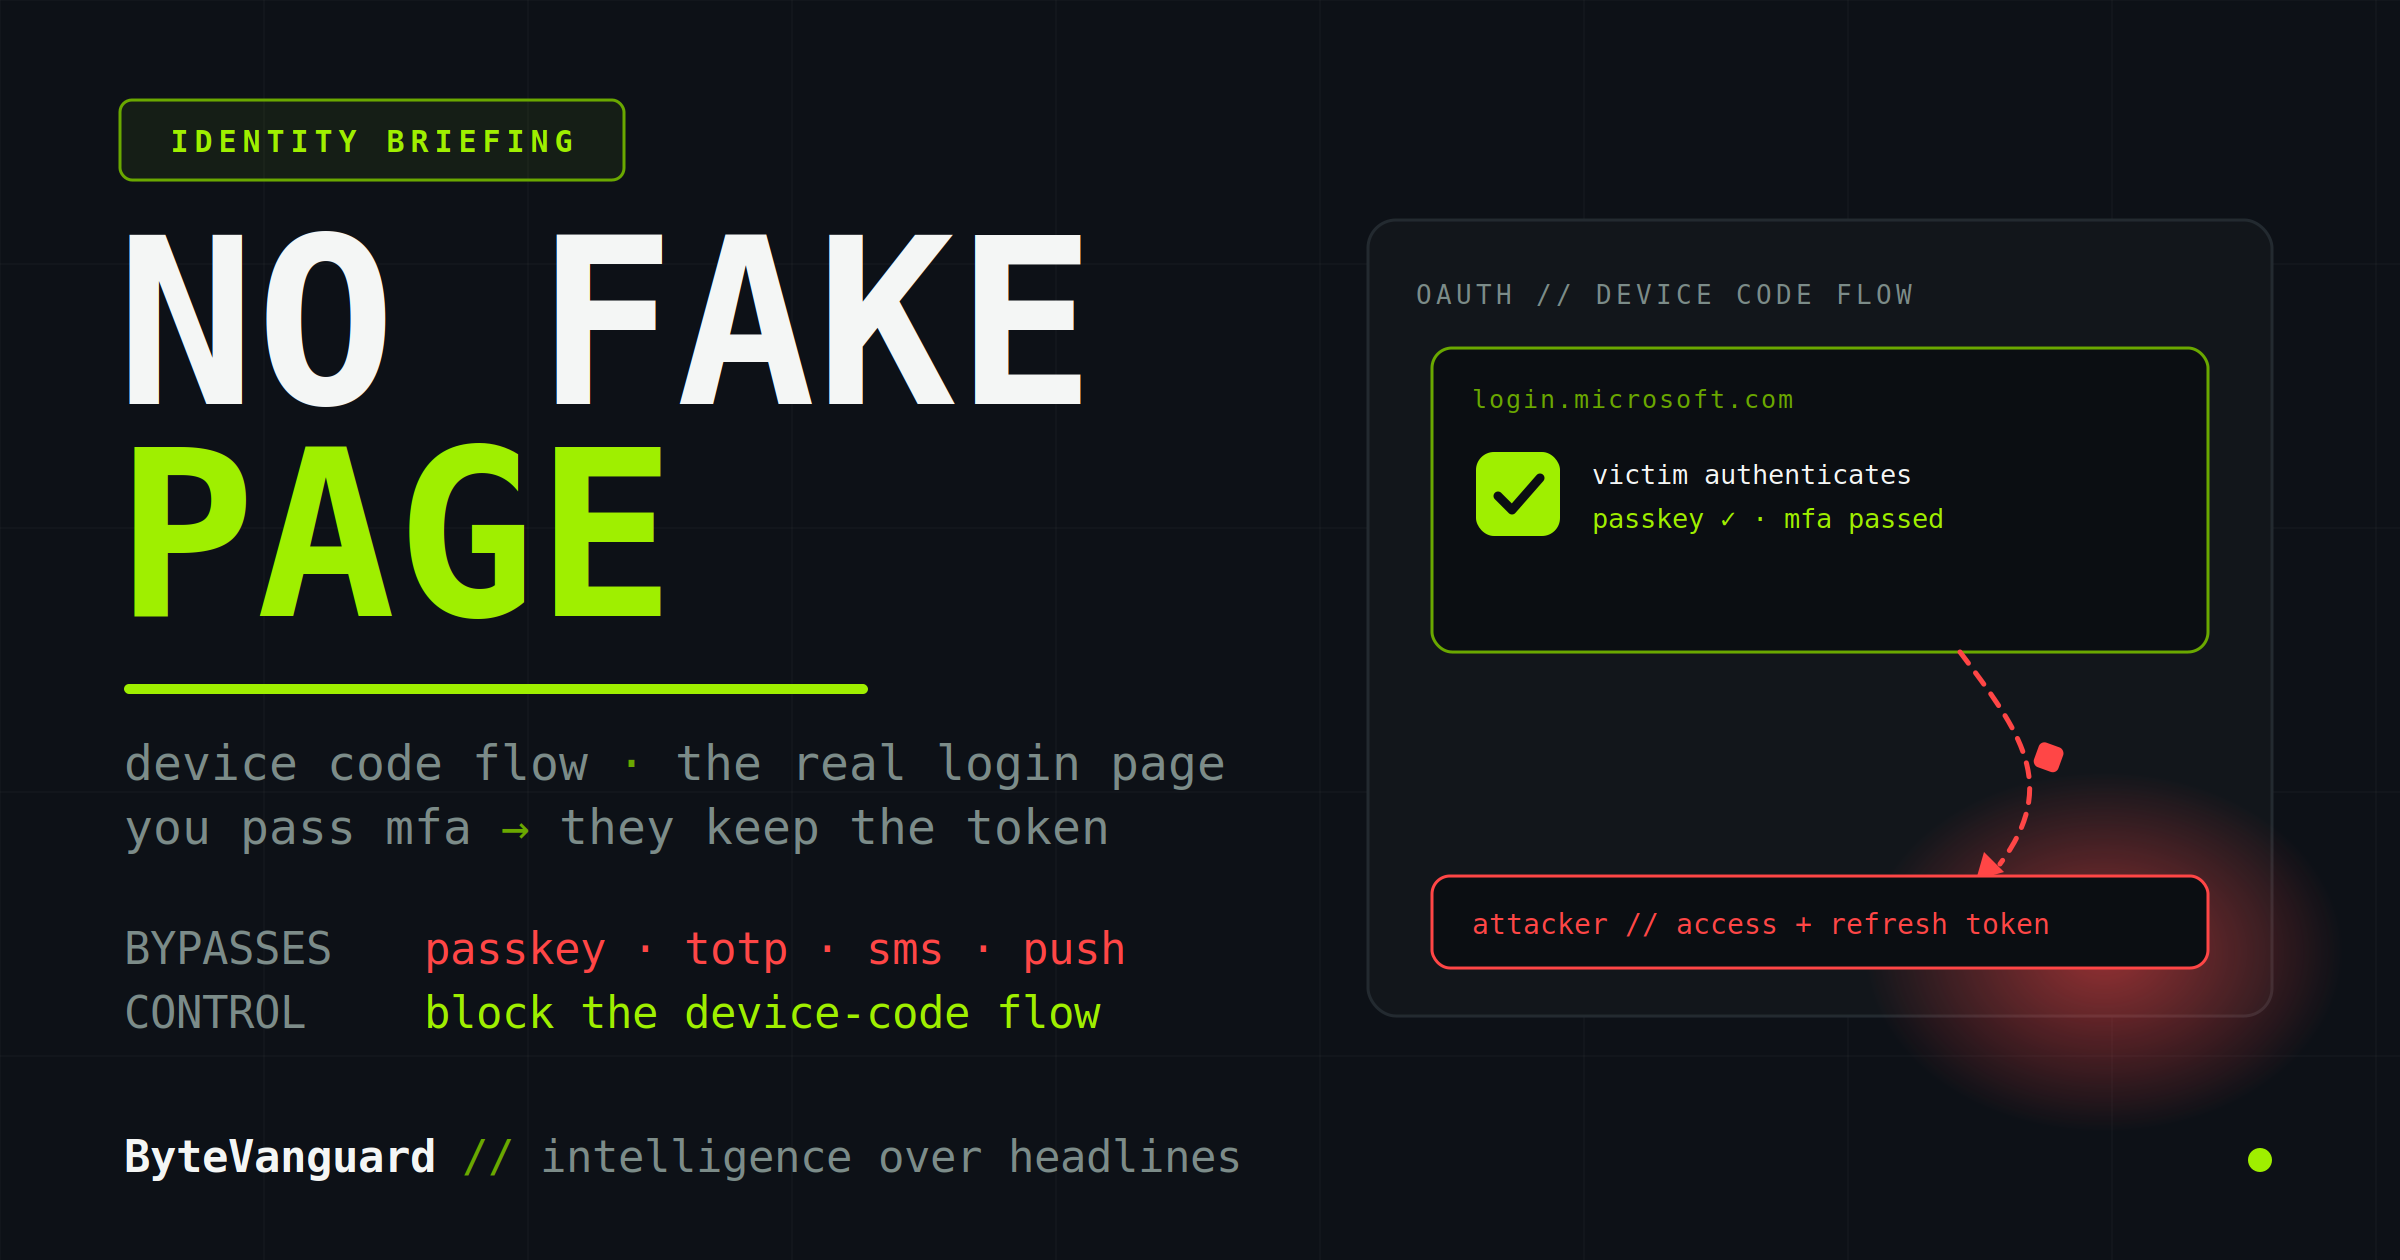
Briefings You can roll out FIDO2 keys to every employee, kill every legacy protocol, and pass every audit — and an attacker can still walk into your Microsoft [...]
Browser-in-the-Middle: The Phishing Technique That Bypasses MFA | ByteVanguard Vulnerabilities Attackers are no longer trying to steal your password. They’re handing you a keyboard — one that belongs [...]
AiTM Phishing: The MFA Bypass Driving Modern Identity Breaches Published: March 6, 2026 | ByteVanguard Threat Overview Adversary-in-the-Middle (AiTM) phishing has rapidly emerged as one of the most [...]
Credential Abuse: Why Logging In Beats Breaking In – 2026 Reality Published: March 3, 2026 | ByteVanguard Executive Summary In 2026, attackers no longer need zero-days. They need [...]
The Threat at a Glance Threat Type Social Engineering + Real-Time AiTM Phishing (Vishing-as-a-Service) Severity High (Effective Bypass of MFA/SSO – Comparable CVSS ~8.2) Affected Systems SSO Providers [...]
Voice-phishing (vishing) toolkits are rapidly proliferating across dark web forums, Telegram channels, and underground cybercrime marketplaces in early 2026. These customizable kits empower even novice attackers to launch [...]