Published: May 6, 2026 AI Agents and KEV are starting to collide with one of the hardest problems in enterprise security: the patch window is getting smaller. For [...]
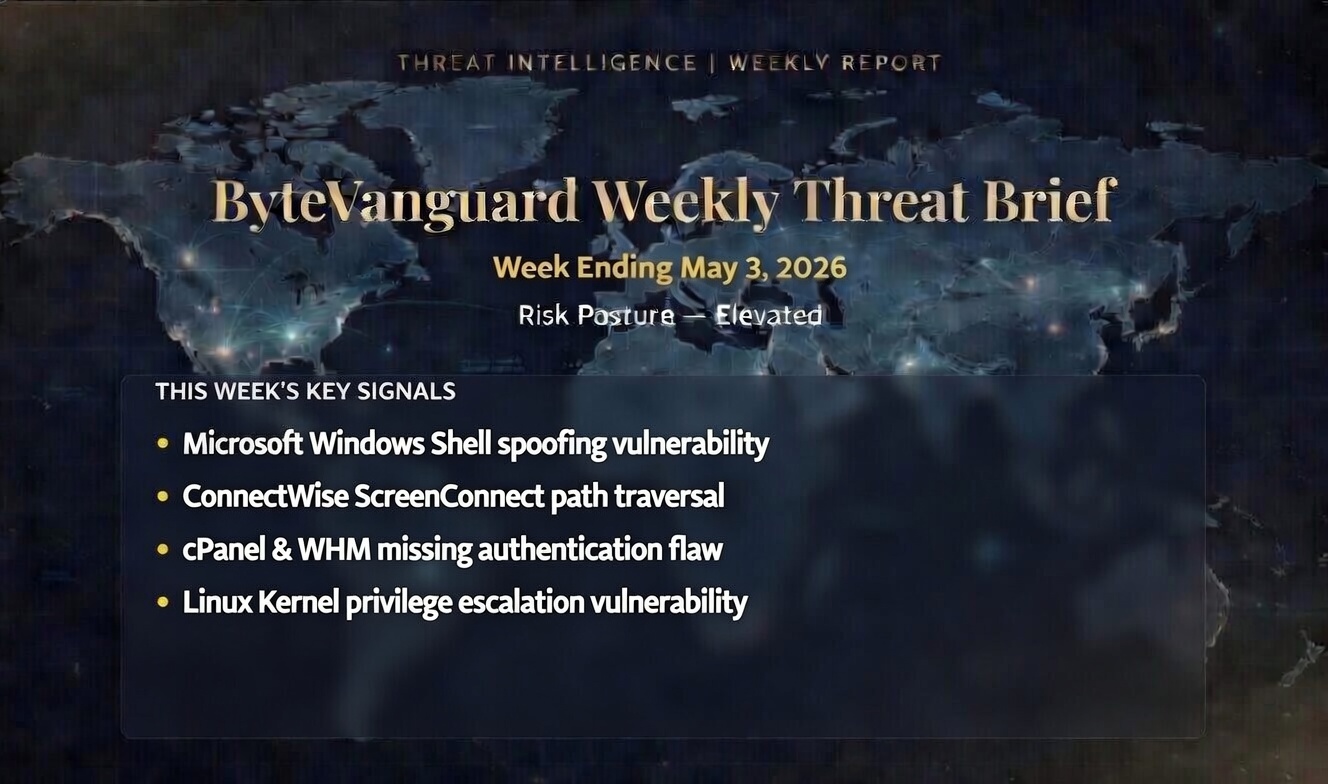
Weekly Threat Brief — Week Ending May 3, 2026 | ByteVanguard Published: May 4, 2026 Overall Risk Posture: Elevated The week ending May 3 was defined by control-plane [...]
Published: May 1, 2026 Remote management planes are having a bad week. Two days after CISA added ConnectWise ScreenConnect to the Known Exploited Vulnerabilities catalog, the agency added [...]
Published: April 29, 2026 Remote management tools are supposed to help administrators control environments at scale. When attackers compromise them, or abuse them after gaining access, they become [...]
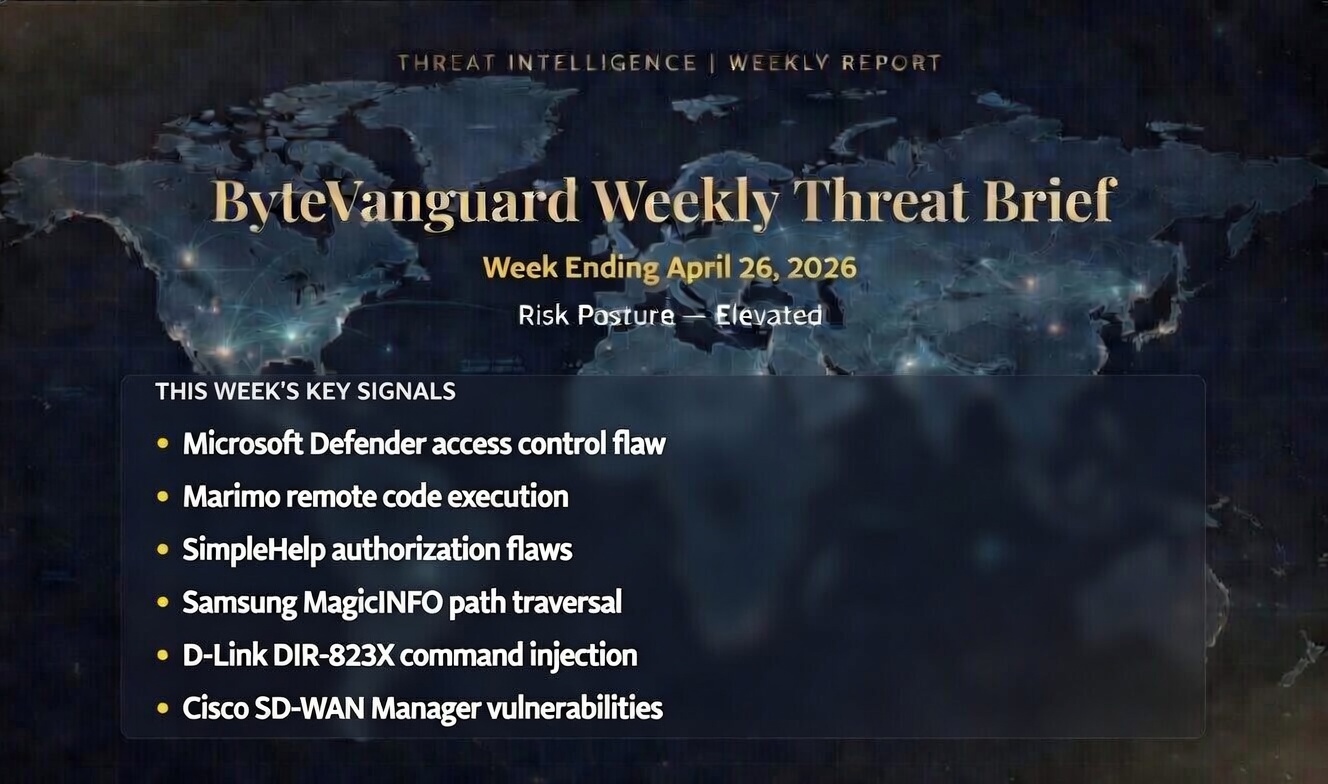
Weekly Threat Brief — Week Ending April 26, 2026 | ByteVanguard Published: April 27, 2026 Overall Risk Posture: Elevated The week ending April 26 was defined by exploited [...]
For years, security teams were trained to look for malware, foreign binaries, and obviously malicious tooling. But living-off-the-land attacks work precisely because they avoid that pattern. Attackers do [...]
Published: April 21, 2026 What Defenders Should Know CISA KEV update: CISA added eight new vulnerabilities to the Known Exploited Vulnerabilities catalog on April 20, 2026, affecting PaperCut [...]
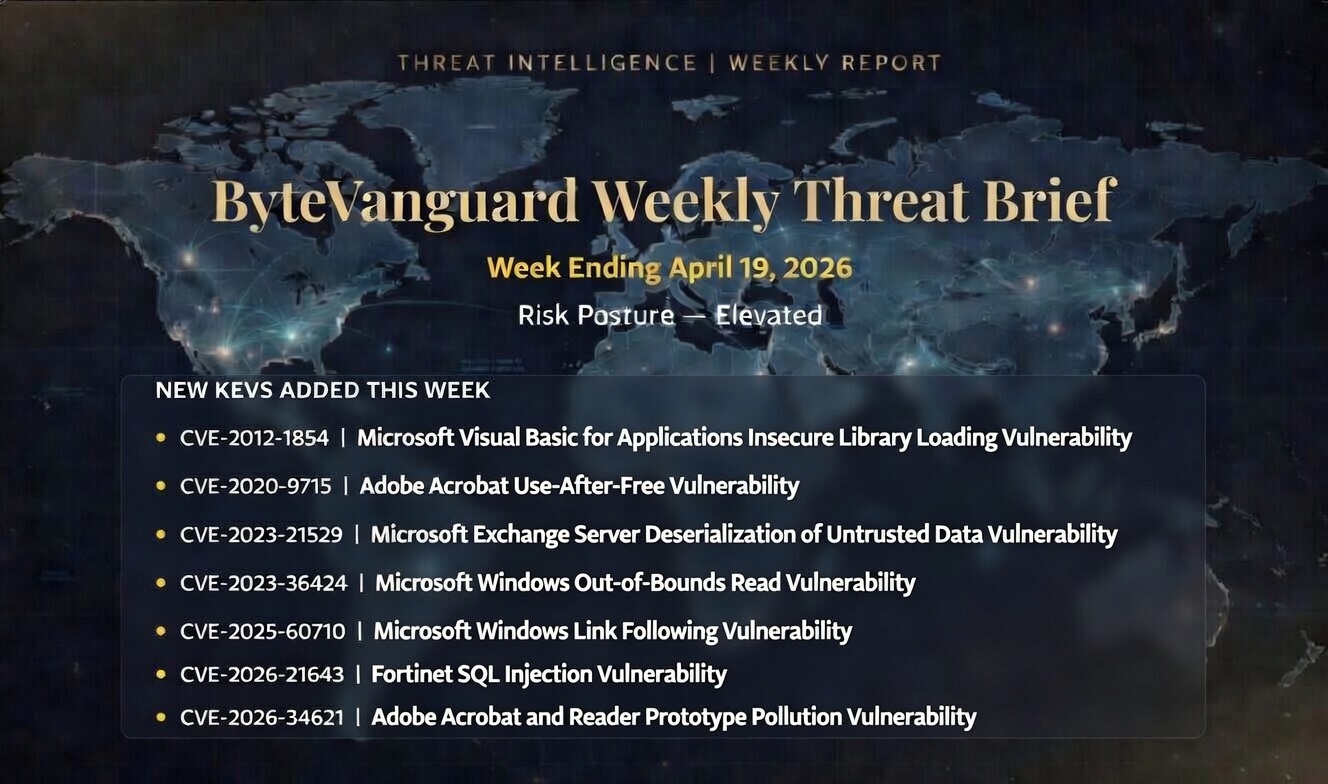
Weekly Threat Brief — Week Ending April 19, 2026 | ByteVanguard Published: April 20, 2026 Overall Risk Posture: Elevated The week ending April 19 was defined by layered [...]
Published: April 15, 2026 The Threat at a Glance Threat Type Large Patch Tuesday release with one exploited-in-the-wild vulnerability, one publicly disclosed zero-day, and a critical pre-auth Windows [...]
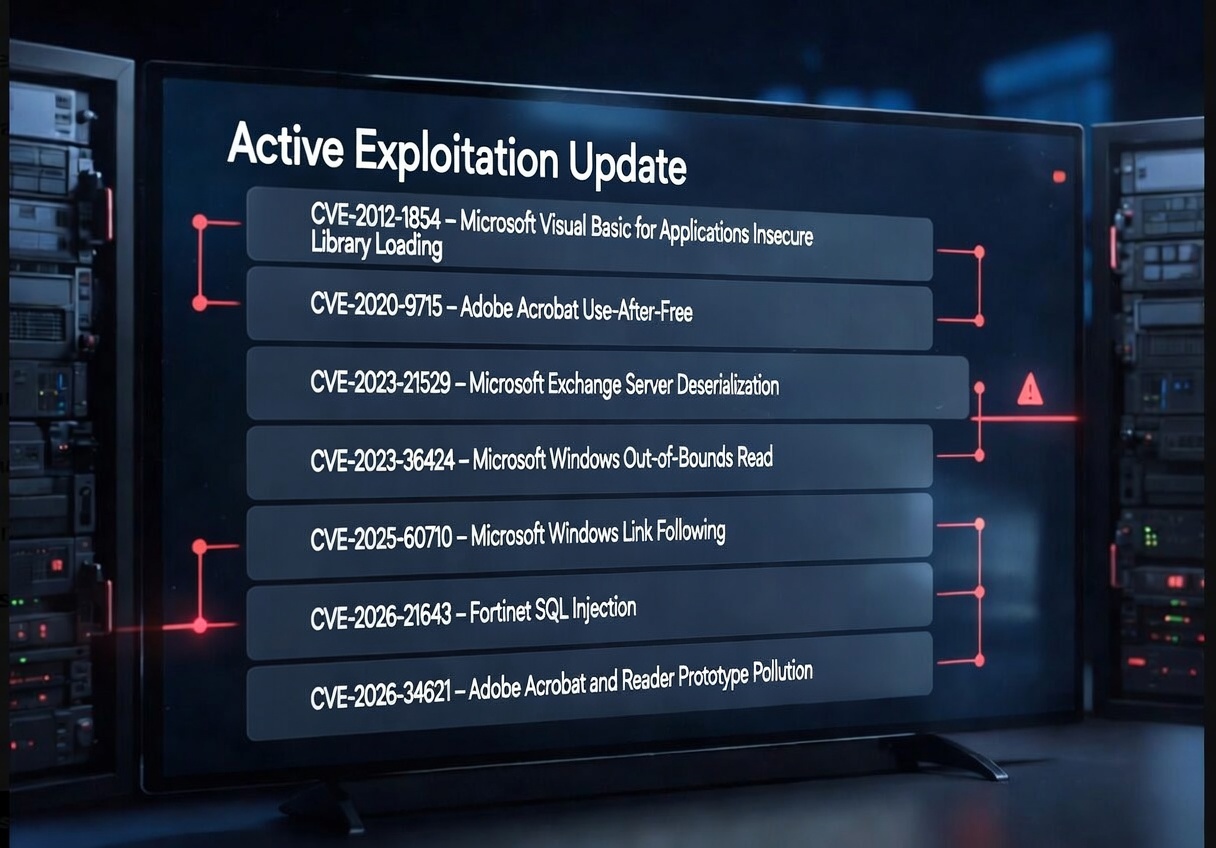
Published: April 14, 2026 CISA KEV Update: On April 13, CISA added seven new vulnerabilities to its Known Exploited Vulnerabilities catalog. On paper, the list looks strange: a [...]